
A vendor risk summary is the board-facing rollup of third-party exposure (posture, concentration, and what changed). Sometimes, the board gets an evidence pack when it asks for a decision view.
Below, you'll find the five sections every risk summary report needs, and a guide to what to include and what to leave out.
What is a vendor risk summary report?
A vendor summary report helps your board decide where third-party risk needs action by condensing vendor exposure into one page, with detail in an appendix. It shows whether exposure is rising or falling, where it's concentrated, and what the board has to decide.
The scope can cover your whole vendor portfolio or a single critical vendor, but the depth stays at summary level either way. Plan to produce one each quarter or on the board meeting cycle, so directors can compare each report against the last.
A vendor risk summary report replaces the ad hoc slide decks of raw findings that often land in board packs. Its readers are directors and executives who own risk decisions but don't work with vendor data day to day.
Vendor risk summary vs vendor risk assessment
A vendor risk assessment is the evidence-gathering work for each vendor, built from questionnaires and control reviews that produce a score. The risk summary is the rollup the board reads, and one assessment can feed many summaries over its life.
When the two merge, the board gets a 40-page pack and spends the meeting on line items instead of decisions. A risk summary report keeps the board on trend and on decisions, while the evidence stays with the team that gathered it.
Each vendor assessment answers a narrower question about one supplier's controls. If you need the assessment that feeds this summary, use our vendor risk assessment guide.
The required sections of a vendor risk summary report
Every vendor risk summary report needs the same five sections, in the same order each cycle. Use this checklist when you build the report:
- Security posture over time: Show the security rating trend across your portfolio and for each critical vendor during the reporting period.
- Critical-risk distribution: Show how exposure spreads across severity bands and business units. Name vendors in the next section.
- High-risk vendors: List the short set of vendors most likely to cause a breach, with an owner and remediation status for each.
- Compliance impact: Flag vendor gaps that affect your obligations under regulations such as GDPR or HIPAA.
- Material public incidents: Note disclosed breaches or major news involving your vendors, and say whether each one touches your data or systems.
Open each section with one line on what changed since the last report, such as a rating drop or a newly critical vendor. That line lets directors read the movement first and decide whether they need the detail underneath.
Board members often ask whether a breach in the news could affect your organization, and the incidents section answers that question. Having the vendor's status and your exposure ready keeps the discussion focused on next steps.
With UpGuard Vendor Risk, curated news and incident feeds surface those disclosures as they happen, so they’re already in the report.
Those five sections cover what a board needs to oversee third-party risk. A finding that fits none of them likely belongs in the assessment file.
What to include and what to leave out
The hardest part of a vendor risk summary is deciding what stays out. The table below sorts common report content into what belongs in the summary, what to leave out, and where each excluded item lives instead:
Keep an appendix ready for directors who ask for supporting detail. An appendix lets you answer follow-up questions without growing the main risk summary report.
How to create an executive report on third-party cyber risk exposure
An executive report on third-party cyber risk exposure follows the same seven steps every cycle. NIST CSF 2.0 gives you a governance anchor for that routine.
The CSF Govern function includes a category for cybersecurity supply chain risk management (GV.SC). The framework is voluntary, but gives directors a recognized reference for how you oversee supplier risk. Follow these steps to build the report:
- Set the scope and audience: Choose the full board or the executive committee, and the whole portfolio or one critical vendor.
- Pull current posture and trend data: Export security ratings for the full reporting period so the board sees direction as well as a snapshot.
- Rank by criticality and concentration: Tier vendors by business impact, then show where critical findings cluster across vendors or business units.
- Isolate residual high-risk items: List what remains after remediation, with a named owner and a due date for each item.
- Map to compliance obligations: Include only the vendor gaps that change your regulatory or contractual exposure this period.
- Add material public incidents: Note disclosed breaches affecting your vendors and whether the incident touched your data or systems.
- Write the "so what" line and the ask: State what the data means in one sentence, then name the decision or risk acceptance you need.
Steps two and three take the longest when vendor data lives in spreadsheets and annual questionnaires. A platform that monitors vendors daily turns that data into an export, leaving you more time to analyze.
Directors act on the ask, so draft step seven carefully. Without a clear request, the board notes the report and moves on, and the residual risk stays where it was.
Scope from step one also determines how much remaining work you need. A single-vendor report can skip the concentration view, while a portfolio report depends on it.
An example of a vendor risk summary
The summary below from UpGuard Vendor Risk shows one section of a board summary report, the critical-risk distribution view.
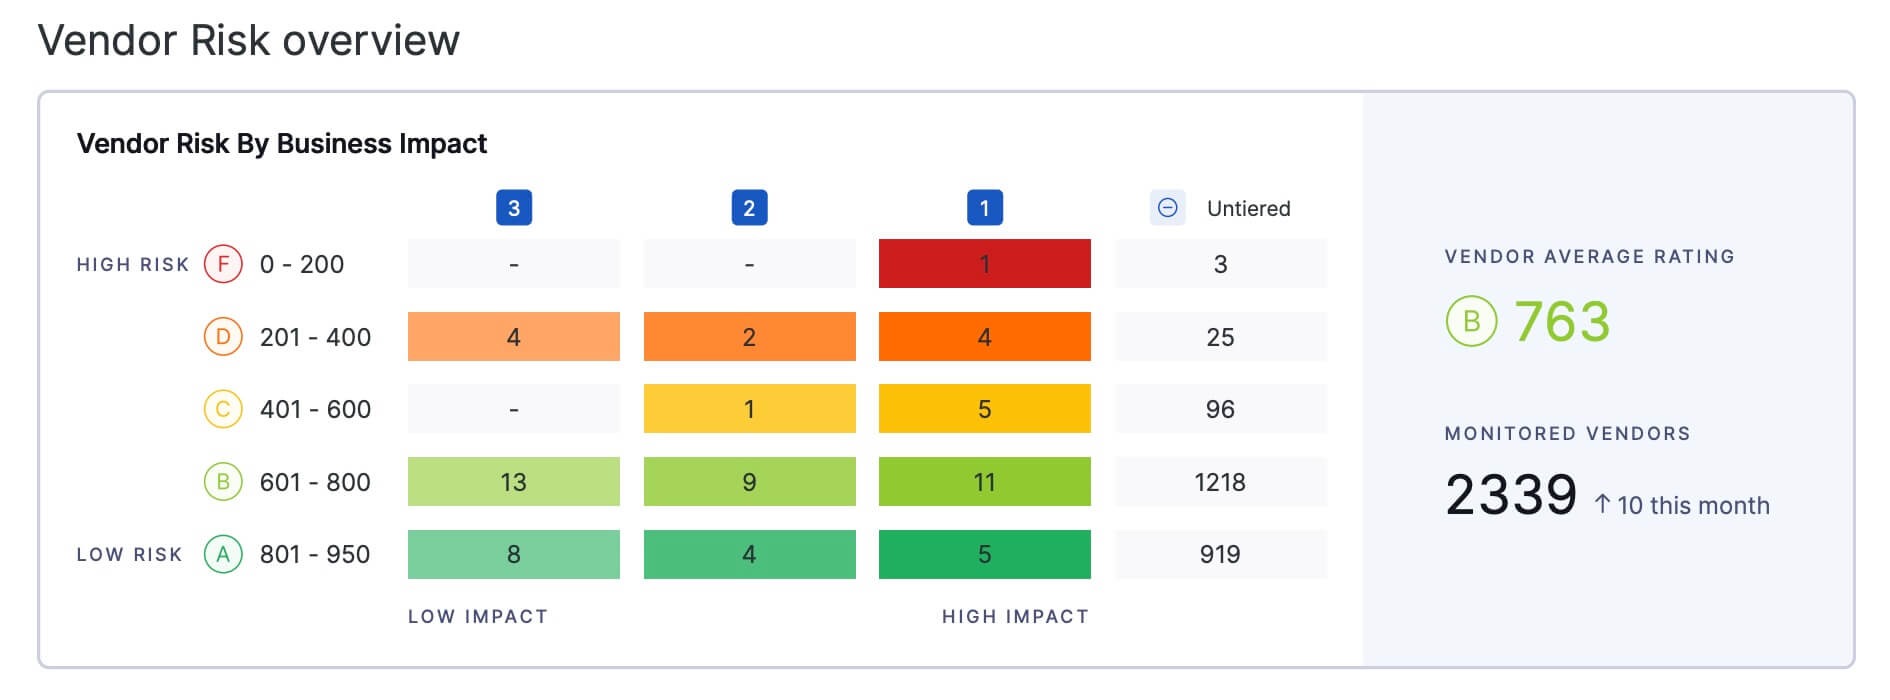
Each callout explains what the element shows and how to present it to the board:
- Severity bands: Risks sort across five severity levels, so directors see the shape of exposure before any vendor names appear.
- Top of the distribution: The critical and high bands draw the board's attention, so point to the high-risk vendors section for who sits there and why.
- Change since last report: Pair the chart with a one-line note on movement, such as fewer critical risks than last quarter.
- Spoken takeaway: Turn the chart into one sentence, such as "Two critical vendors hold most of our high-severity exposure, and both have remediation dates."
Every section of a vendor summary can follow the same pattern, combining one visual with a change note and a spoken takeaway. Directors then learn where to look, and each new report reads faster than the last.
Writing for a board and executive audience
Put the decision first, with the ask and the "so what" line on page one. The five sections then support that decision instead of competing with it.
Translate scores into business terms, such as the revenue process or customer data a vendor touches. A rating drop matters to directors once you tie it to the operations at stake.
Keep the main report to one page plus an appendix, and use the same format every quarter. NACD guidance recommends reporting cyber risk to the board at least quarterly. Consistency lets directors read trends at a glance instead of relearning the layout each time.
Define any term the board may not know, or replace it with plain language. Fourth-party risk, for example, becomes "risk from our vendors' own suppliers."
For US public companies, board reporting also connects to disclosure rules the US Securities and Exchange Commission adopted in 2023. Regulation S-K Item 106 requires public companies to describe, in their reports, how the board oversees cybersecurity risk and whether they have processes to manage third-party risks. A consistent quarterly risk summary report documents how that oversight works in practice.
How UpGuard helps you report vendor risk to the board
UpGuard Vendor Risk connects the vendor data behind your summary to the reports your board reads. These capabilities support each step of the process:
- Built-in reports: Choose from 14 built-in reports to send on demand or on schedule, so the board pack stays current.
- Board-ready summaries: Create a summary in just three clicks from the vendor data you already monitor.
- Board presentations: Generate editable PowerPoint presentations with dynamic, pre-filled commentary, so your first draft starts with context in place.
Chemist Warehouse uses these reports to brief its leadership team. Nigel Hedges, the company's Chief Information Security Officer, describes the value: "Executive teams don't want to see raw security data — they want insights. UpGuard gives us structured, visual reports that make it easy to communicate risk levels to leadership and drive decision-making."
When your vendor data stays current, the quarterly summary becomes a review step. Book a demo to see how UpGuard Vendor Risk turns vendor monitoring into a board-ready risk summary report.
Related posts
The Evidence Is In: UpGuard Named a Leader in the IDC MarketScape for Worldwide Third-Party Risk Management
