
Vendor tiering allocates third-party review effort by classifying each vendor so assessment depth and review cadence match business impact and security exposure. Instead of treating every supplier as a critical relationship, you sort your vendor portfolio so questionnaires, reviews, and monitoring intensity match the tier.
A vendor tiering process is an end-to-end workflow: capture exposure at intake, assign the tier, match the tier to diligence depth and reassessment timing, and promote or demote when scope changes.
This article explains a five-tier model with examples, the intake questionnaire behind it, the security-risk method for assigning tiers, and how Vendor Risk supports the workflow.
Vendor tiering model: a tier-by-tier breakdown
A practical vendor risk tiering model maps each tier to a vendor type, a primary risk driver, and a review cadence so the label decides work.
A tier one vendor has the deepest inherent and residual risk work because failure impacts availability, regulated data, or both. That risk usually means executive sponsorship for exceptions, evidence-heavy control testing, and the shortest re-tier window in the portfolio.
Tier two relationships still justify full assessments on a tight cycle when identity, workforce, payment, or regulated data sits with the vendor, even if the business could survive a short outage.
Tier three covers tools your teams depend on daily without crown-jewel access. Standard questionnaires and periodic review are enough when the primary risk is moderate process dependency rather than systemic outage.
Tiers four and five free analyst capacity so critical and high relationships receive adequate attention instead of equal scrutiny across the whole vendor inventory.
That analyst capacity is expensive. An EY study found 52% of organizations spend 31 to 60 days on third-party assessments. Run that assessment depth across an untiered inventory and months of analyst time go to relationships that never warranted it.
A webinar registration tool with limited blast radius shouldn’t get the same questionnaire depth as a customer support platform. A single-seat research subscription with no system access should clear intake and wait for renew-only checks.
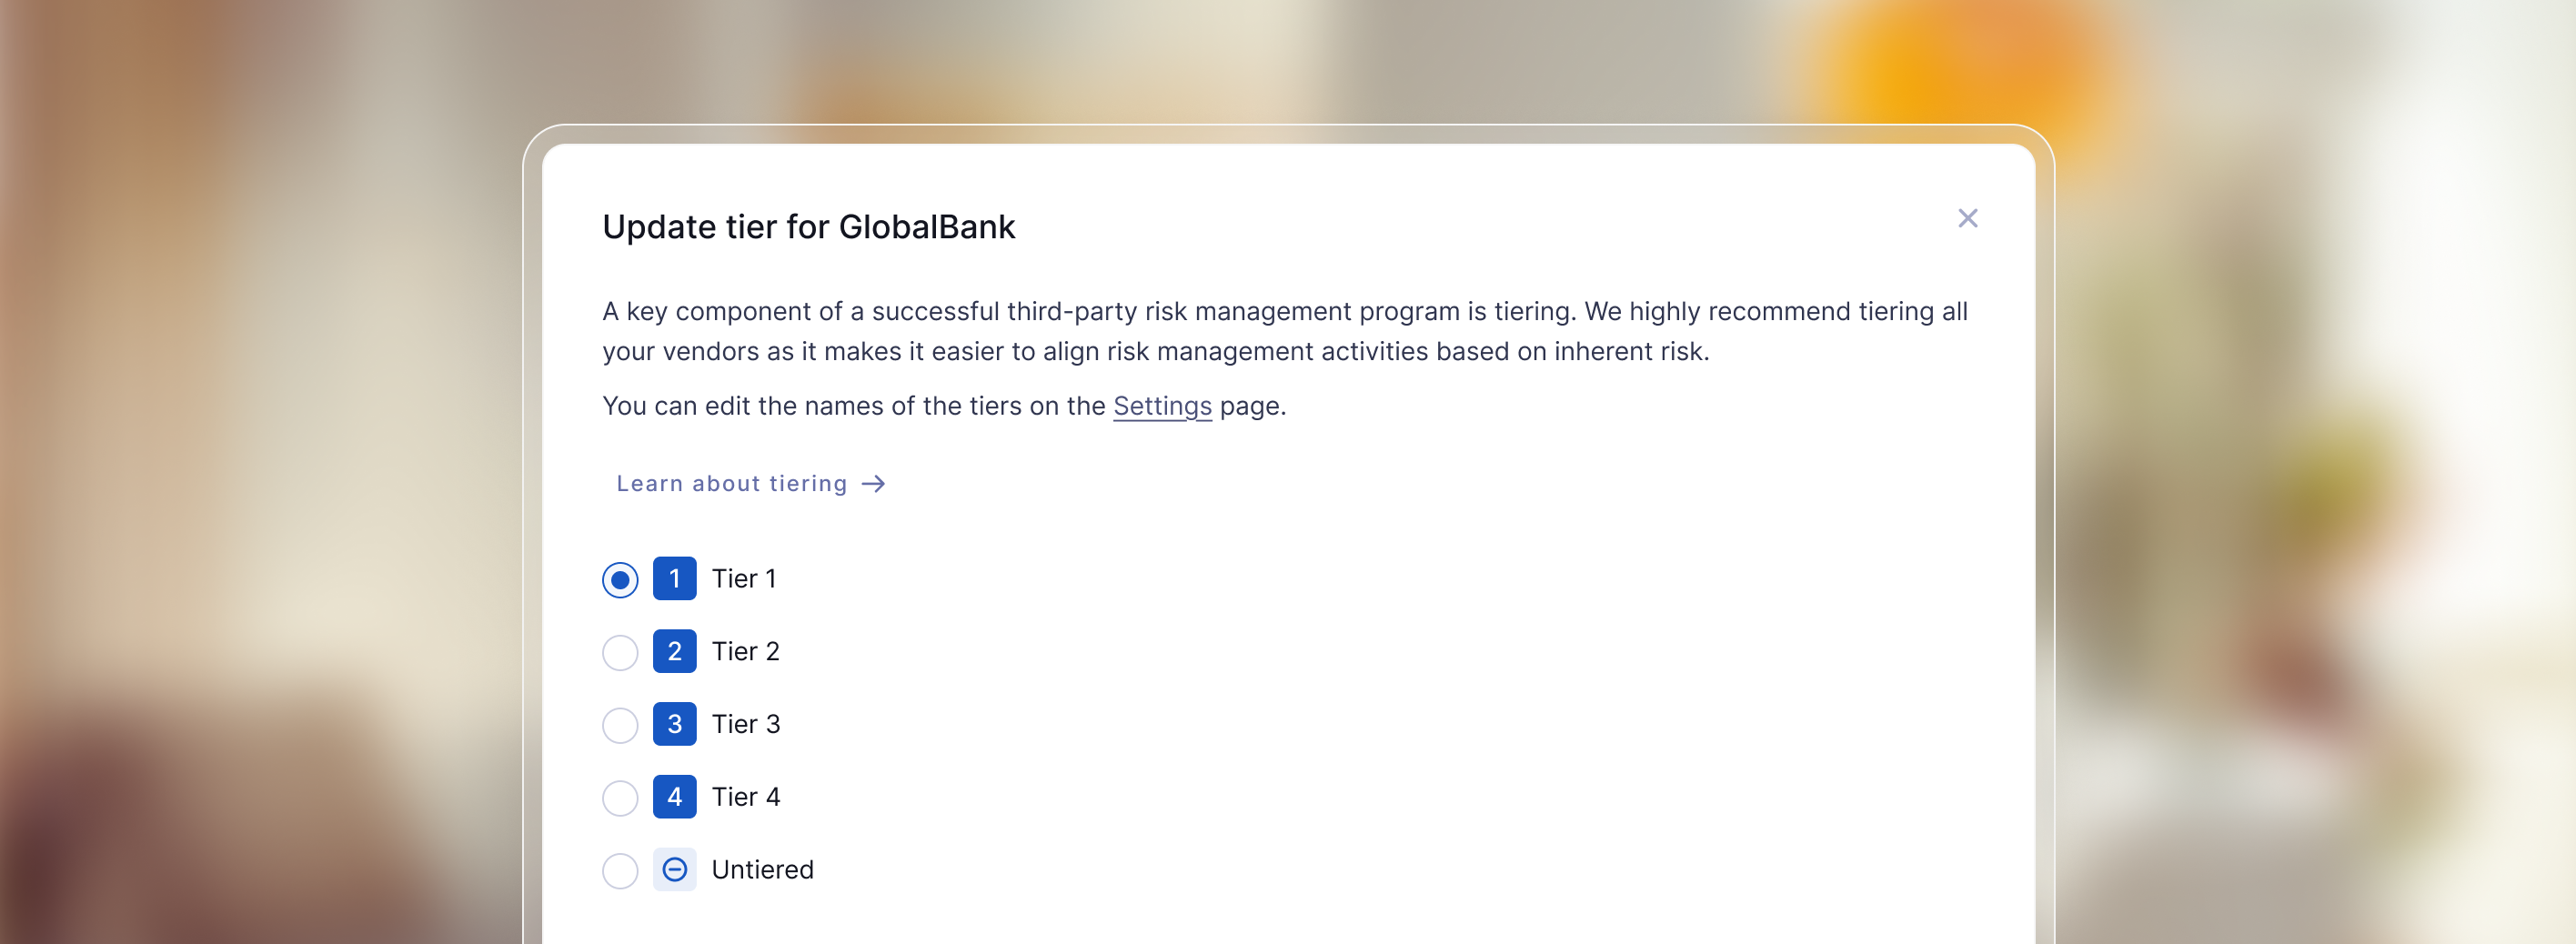
Treat tiers as living classifications. When a medium-tier project management platform starts holding production personally identifiable information or becomes a single point of failure for a core process, promote it. When a critical relationship loses privileged access or exits a regulated workflow, demote it. The model only works when scope changes move the tier and the review depth together.
Vendor Risk lets you implement a model like this with default or customizable tiers, portfolio tags, and custom vendor attributes, then attach assessment templates to each tier so review depth and cadence follow the tier. Start a free Vendor Risk trial to see tier-aligned assessments against your own vendor list.
Vendor tiering questionnaires
A vendor tiering questionnaire captures observable exposure at intake (data types handled, system access, operational criticality, and regulatory flags) and scores those answers into a tier. It’s the intake instrument for classification, not a substitute for residual-risk testing once you’ve set the tier.
Keep questions observable and repeatable so two analysts reach the same tier for the same facts.
Understand questionnaire design and scoring criteria in our vendor tiering program guide.
How to tier vendors by security risk
Tier vendors by security risk using five observable criteria: data access, operational continuity, regulatory mandates, strategic exposure, and security resiliency. Then, match each resulting tier to review depth.
Those five criteria are Vendor Risk’s internal methodology for inherent-risk classification. Score what the vendor can touch and how badly operations fail if it drops.
Use them to decide the tier first, and expand residual controls only after you’ve set the label. For the full mapping method, see how to map vendor tiers to inherent risk.
How many tiers should you use?
Start with three tiers, or five once your portfolio justifies it. Fewer than three tiers puts critical and commodity relationships into one bucket, so both compete for the same queue.
More than five often adds admin cost without clearer decisions. Analysts debate tier three A versus three B while assessment templates stay identical.
A five-tier model (critical through transactional) fits when you need an explicit screen-only bucket for negligible relationships. A three-tier model works when the portfolio is small, and every label still changes questionnaire depth or cadence.
Whichever model you choose, document the decision rule once, apply it to every new vendor, and re-tier when access or criticality changes. If two labels never produce different evidence requests, merge them.
Does tiering replace continuous monitoring?
Tiering and continuous monitoring do different jobs. Continuous monitoring surfaces change, such as a new vulnerability on an internet-facing asset, a control score drop, a leaked credential, or a shift in fourth-party dependency.
Tiering decides review depth and how fast you respond when that change appears. A static label without monitoring goes stale within a week of onboarding.
Monitoring without tiers burns equal effort on every vendor, including the research subscription relationship that never touches production systems.
Continuous monitoring tells you when something changed, but tiering tells you how much attention to pay. Vendor segmentation that ties tiers to blast radius makes the split concrete when supply-chain incidents spread through shared providers.
Manual vs automated tiering
Manual tiering works while inventory is small and scope rarely changes. It fails when contracts, integrations, and data paths move faster than a spreadsheet owner can update rows. Automation should apply the same documented criteria and promote or demote when access or criticality changes.
It shouldn’t invent opaque scores nobody can defend to an auditor. For larger ecosystems that need weighted scoring and workflow scale, use a weighted-model implementation rather than stretching a three-label spreadsheet past its breaking point.
How UpGuard Vendor Risk supports tiering
Vendor Risk prioritizes by vendor criticality and tier-aligned assessment templates so inherent-risk labels change review depth, not just the tag.
You discover and onboard vendors, then run tier-aligned assessments. Findings route through remediation and into board-ready reporting.
Take a Vendor Risk product tour to see how the platform keeps the tier-to-diligence link in one workflow.
Frequently asked questions
What is a vendor tiering process?
A vendor tiering process classifies third parties by business impact and security exposure, assigns a tier label, and matches that label to assessment depth and review cadence. You re-tier when access, criticality, or regulatory scope changes so the label still matches the work the vendor requires.
What is an effective vendor risk tiering model?
A five-tier model runs critical (identity provider) through high (customer support platform), medium (project management tool), low (webinar registration), and transactional (industry research subscription), each with a primary risk driver and a different review cadence.

