
Two analysts review the same vendor and decide on different tiers. One labels it high, the other medium, and the rule that got them there is unclear. The label sticks anyway, and assessment depth follows it. This inconsistency is what tiering without a specific method costs you. When placement depends on who handled the intake form, contract value and brand familiarity become the deciding factors, instead of data access and business dependency.
A well-known platform with a large invoice lands in the highest tier, while a low-spend tool with production system access and a copy of your customer records sits two tiers below it, on a lightweight review.
When an auditor asks you why a vendor was scored medium, you need a defensible rule and method you can show them.
If you need to know what vendor tiering is, begin there. This article covers the scoring process you can run week to week so review depth matches inherent risk, and how UpGuard Vendor Risk keeps review depth aligned to the tier.
How to tier vendors by security risk
To tier vendors by security risk, score five observable criteria with fixed weights. Weight data access at 40% or more, then score operational continuity, regulatory mandates, strategic exposure, and security resiliency. Apply a fixed tier cut-off to the weighted total.
Enforce a critical override when a vendor breaches any single hard threshold, and treat the formula as the default; then log every override with an owner, a review date, and an approver.
A security risk model turns tiering into a decision process you can run next week. You collect the same facts for every vendor, score the same criteria, and only then decide diligence depth. Spend, brand familiarity, and "the team has always used them" stop driving the tier.
UpGuard Vendor Risk keeps the categorization and any override on the vendor record, so the reasoning holds up at the next review and doesn’t leave with the analyst who made the tiering decision.
The five-criteria vendor tiering model
Vendor Risk uses this five-criteria model internally, which draws on customer tiering programs.
The remaining 60% of the suggested weight divides evenly across the other four criteria. Adjust only through governance, and document the change.
Score each vendor against these five criteria:
- Data access: Carries the most weight because unauthorized disclosure and misuse scale with what the vendor can touch. A payroll processor holding employee records carries more risk than a facilities vendor with no system access, even when contract values look similar.
- Operational continuity: This criterion captures dependency. If the vendor becomes unavailable, can core services continue, or does customer delivery stop? Score the recovery impact instead of the invoice size.
- Regulatory mandates: This applies when regulations require specific evidence and control expectations. A cloud tool that processes cardholder data brings PCI DSS scope into the relationship whether the vendor seems low risk or not.
- Strategic exposure: Covers concentration and reputation. A single identity provider or core SaaS platform may deserve a higher tier. The same goes for a customer-facing integration, even when day-to-day data volume is only moderate.
- Security resiliency: This is the posture signal, covering control maturity and known gaps, as well as how the vendor responds to findings. It informs residual risk after you set inherent exposure, and it shouldn’t replace the inherent-risk criteria we’ve outlined above.
Assign each criterion a consistent scale, whether that’s one to five or zero to 100, then multiply each score by its weight and total them. Map the total to fixed bands such as critical, high, medium, and low, and publish the bands in your cybersecurity procedures so two analysts produce the same tier from the same inputs.
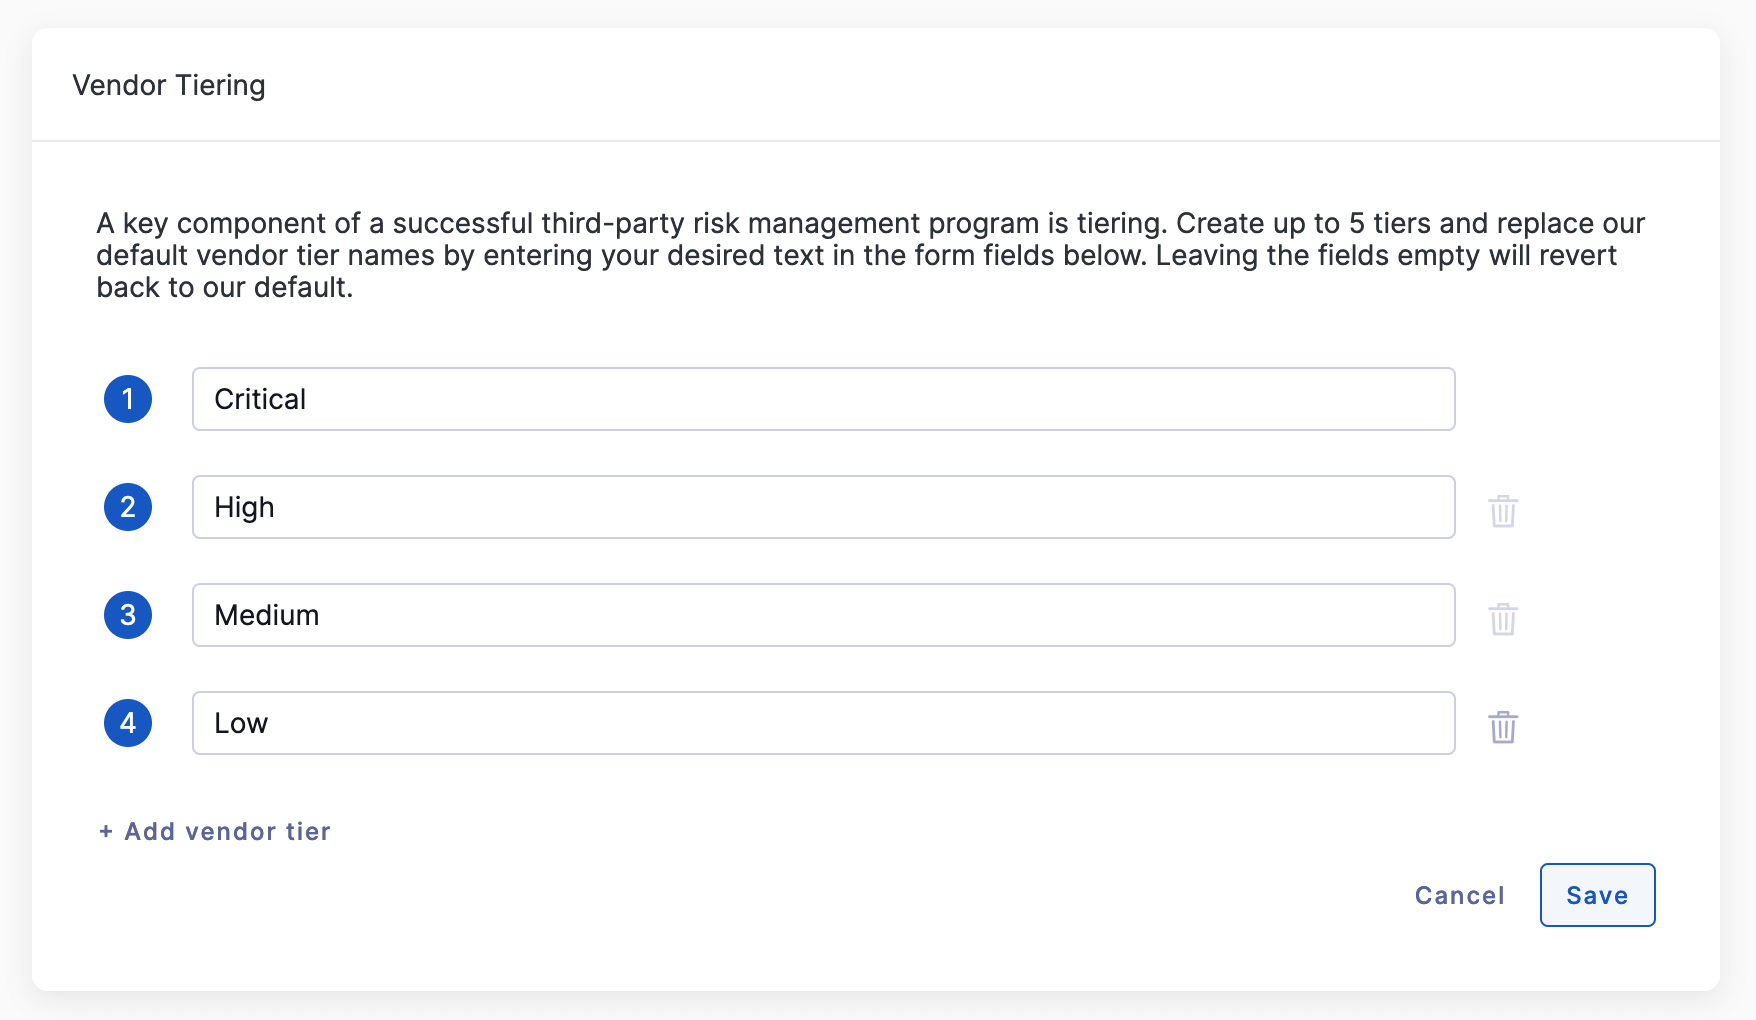
Critical override means a single hard threshold forces the vendor up a tier, or straight to critical, even when the weighted total is lower. Examples include unrestricted production data access, sole-source dependency with no workable backup, or a regulatory scope you can’t accept at a lighter review depth. Overrides that raise a tier without a logged reason defeat the model's purpose.
Once you set the tier, map vendor tiers to inherent risk. That's what should decide assessment depth, evidence requirements, and review cadence, not just what sits on the vendor's record. A tier only pays off if vendor risk assessment gets deeper as the label goes up.
What's the most efficient way to score and tier vendors by risk level?
Use a short weighted score across five criteria. Keep data access at 40% or more, apply a fixed tier cut-off to the total, and enforce a critical override for any single-criterion hard-threshold breach.
Run the same workflow on every intake:
- Capture facts: Gather data types and volumes, systems touched, business services supported, regulatory scope, concentration, and known posture signals.
- Score criteria: Use one scale and written scoring notes so "four" means the same thing next quarter.
- Apply weights: Keep data access at or above 40% of the model, and keep remaining weights uniform unless governance revises them.
- Apply the cut-off: Convert the weighted total into a tier band.
- Check overrides: Test hard thresholds, raise the tier if one fires, and record why.
- Set review depth: Match the tier to questionnaire depth, evidence requirements, and monitoring cadence before anyone signs the contract.
A one-page scoring sheet creates efficiency. If two reviewers can’t reach the same tier from the same packet, shorten the rubric and tighten definitions before you add more questions.
For larger vendor portfolios, keep the same weights and automate intake, re-score triggers, and portfolio views. Don’t invent a second model per business unit. Programs that need that operating pattern can follow vendor tiering that scales without abandoning the formula-first rule.
Three vendor tiering best practices
In day-to-day third-party risk management (TPRM), three best practices succeed:
- Security ratings: Use external posture scores to pressure-test residual risk and re-tier signals alongside inherent-risk scoring.
- Framework mapping: Map tier-driven evidence and questionnaire depth to the frameworks your program already runs.
- Vendor expectations: Set contractual and operational expectations by tier before the relationship hardens.
These vendor tiering best practices supplement the scored model. The model assigns the tier, while these practices keep the tier honest, auditable, and enforceable.
Inside the wider TPRM lifecycle, the stages run discovery, onboarding, assessment, ongoing risk management, continuous monitoring, then offboarding. Place tiering after discovery and onboarding, and before assessment and continuous monitoring.
Use security ratings to pressure-test posture
Vendor Risk security ratings turn the full external scan into a single comparable score, and you can review it at intake and on a schedule. Trigger re-evaluation when a score drops past a defined amount. Don’t let a strong rating justify a lower tier when data access, continuity issues, or regulatory scope say otherwise.
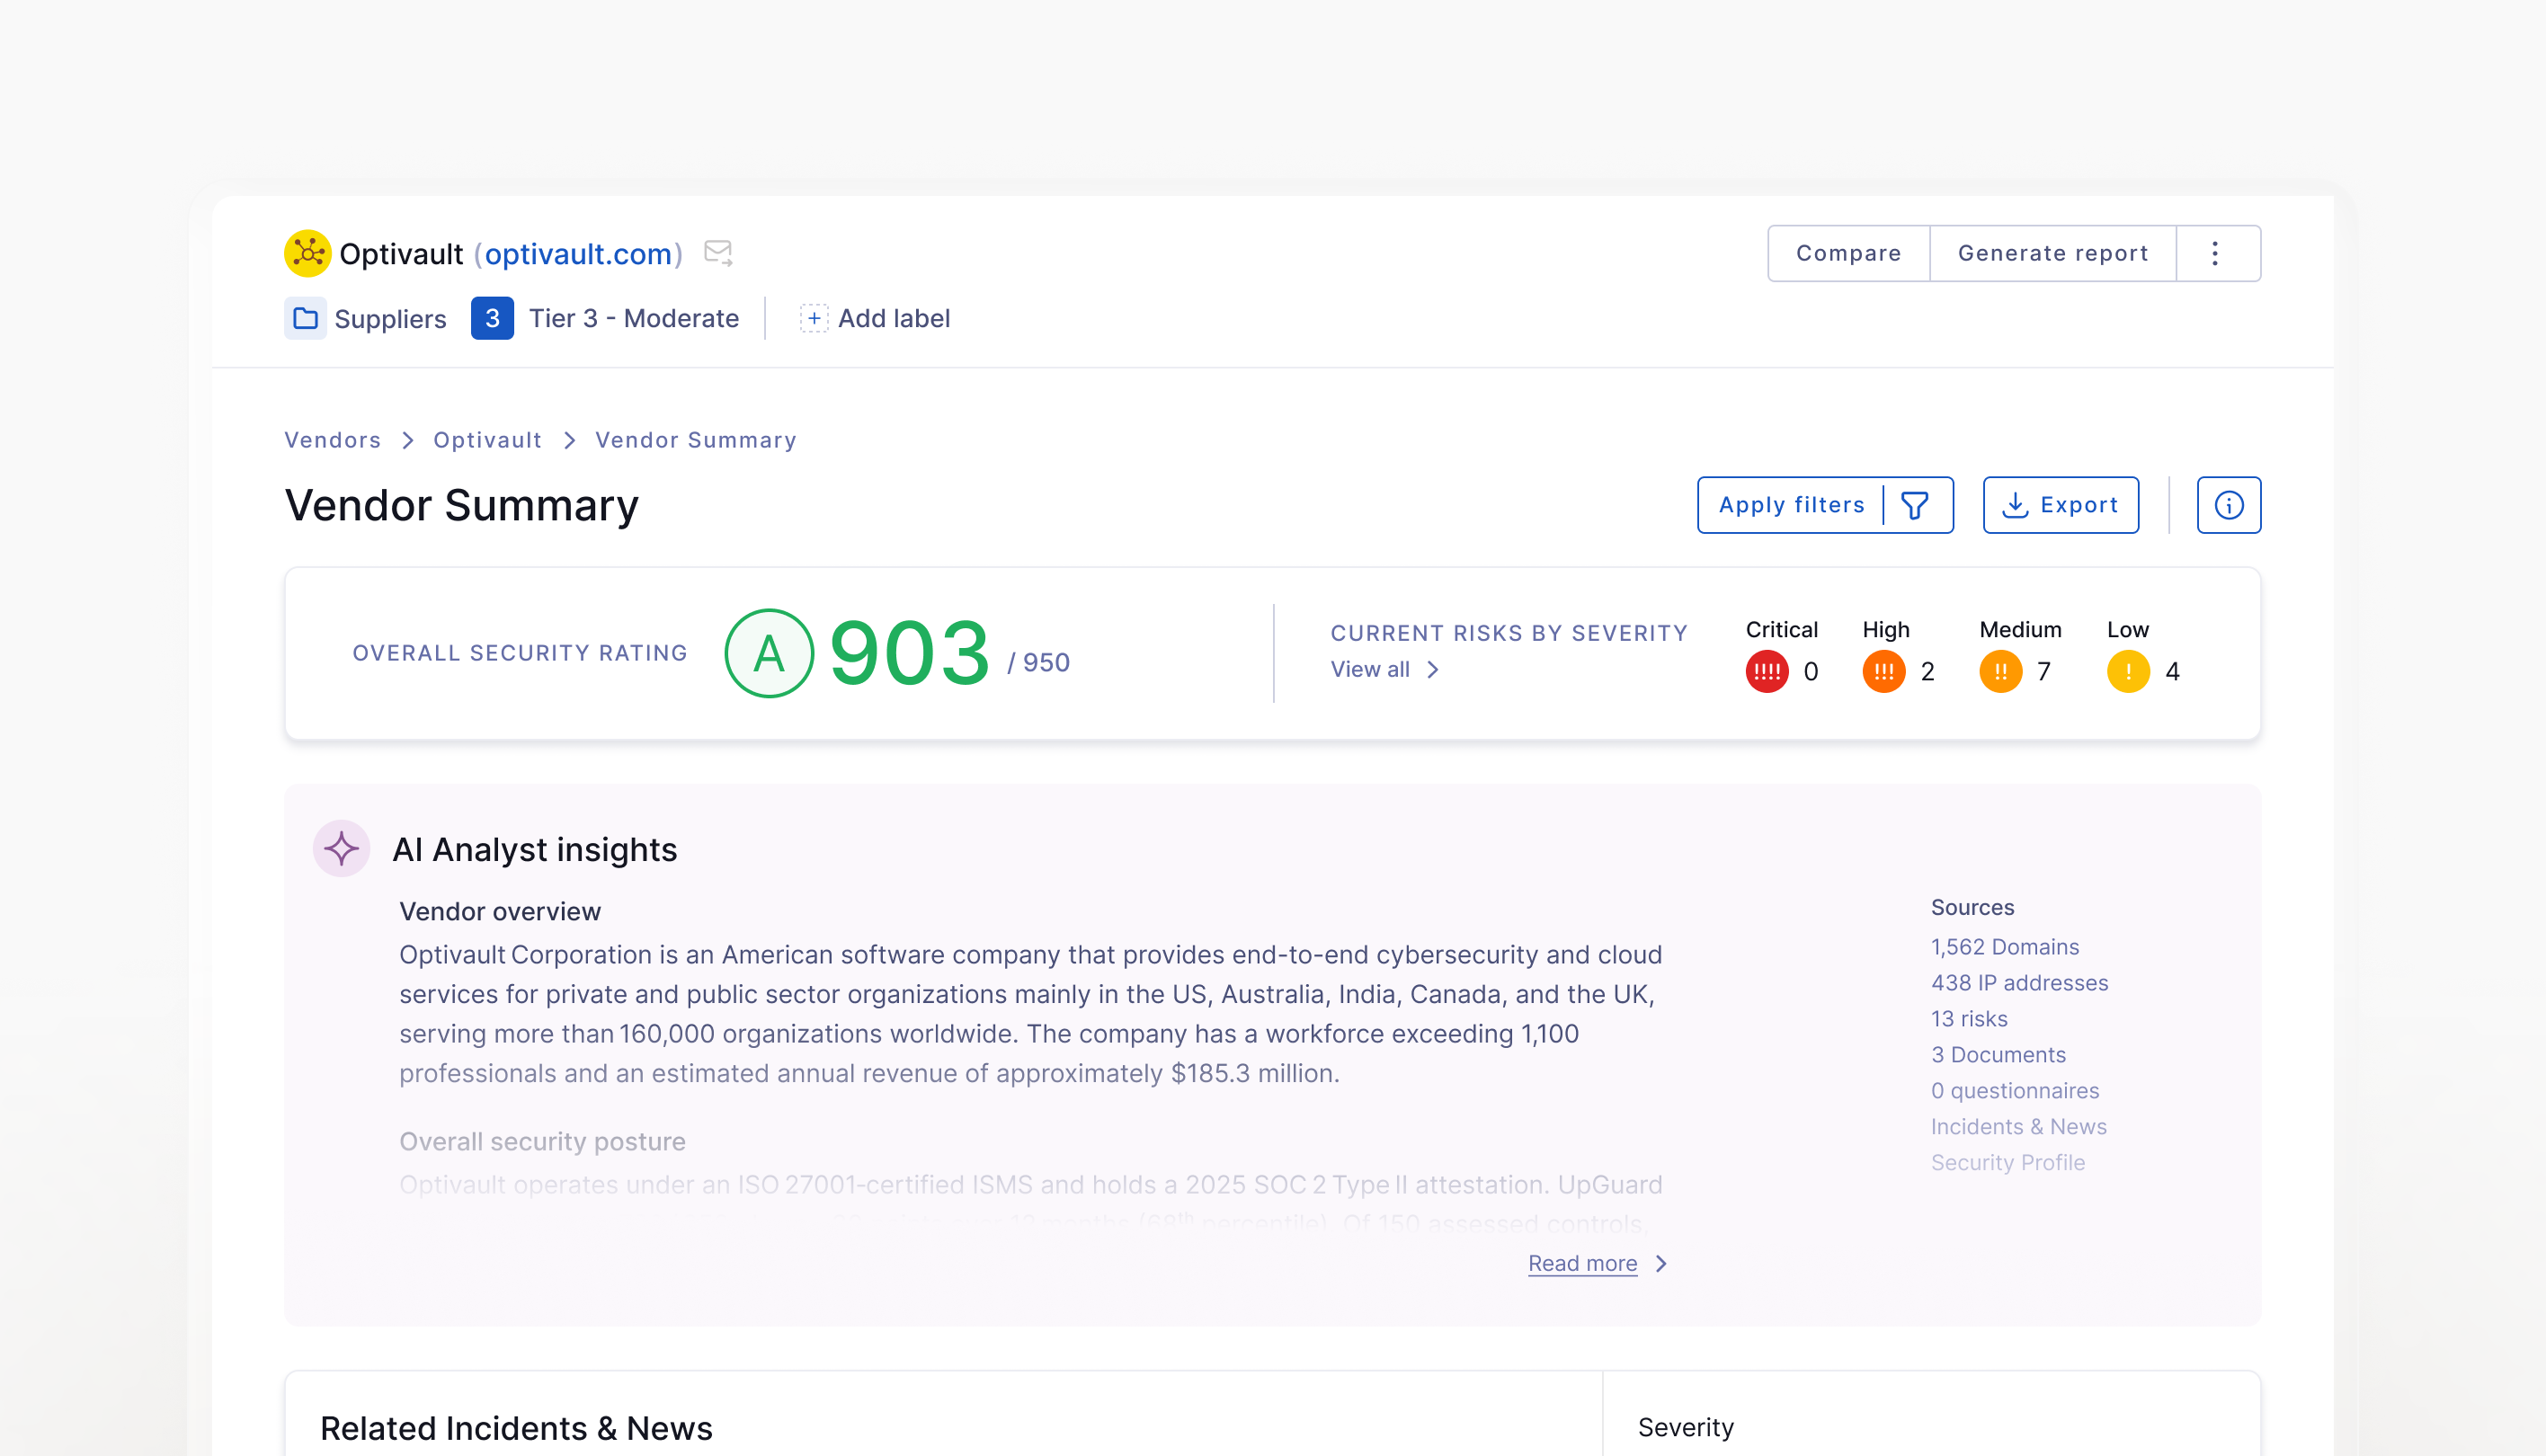
Combine the rating with the five-criteria score, and then decide whether posture evidence changes residual treatment inside the tier or forces a logged override. Next, define the rating move that requires a re-tier review. Without a rule, tiers become outdated while exposure changes.
You can keep security ratings beside your inherent-risk tier in Vendor Risk so a posture drop can trigger re-review without rewriting the five-criteria score.
Map assessment depth to security frameworks
Tier labels only help auditors when they change what you ask for. Critical and high tiers should require deeper evidence.
The deeper evidence set includes fuller questionnaires, recent SOC 2 reports on security controls, ISO 27001 certification evidence where relevant, tighter control sampling, and clearer ownership of open findings. Lower tiers can use shorter forms and lighter evidence. Map responses to frameworks your program already uses.
Common frameworks include ISO 27001, SOC 2 reports, PCI DSS payment card requirements, and sector regulations. NIST CSF 2.0 is the version to map against if supplier criticality is part of your program.
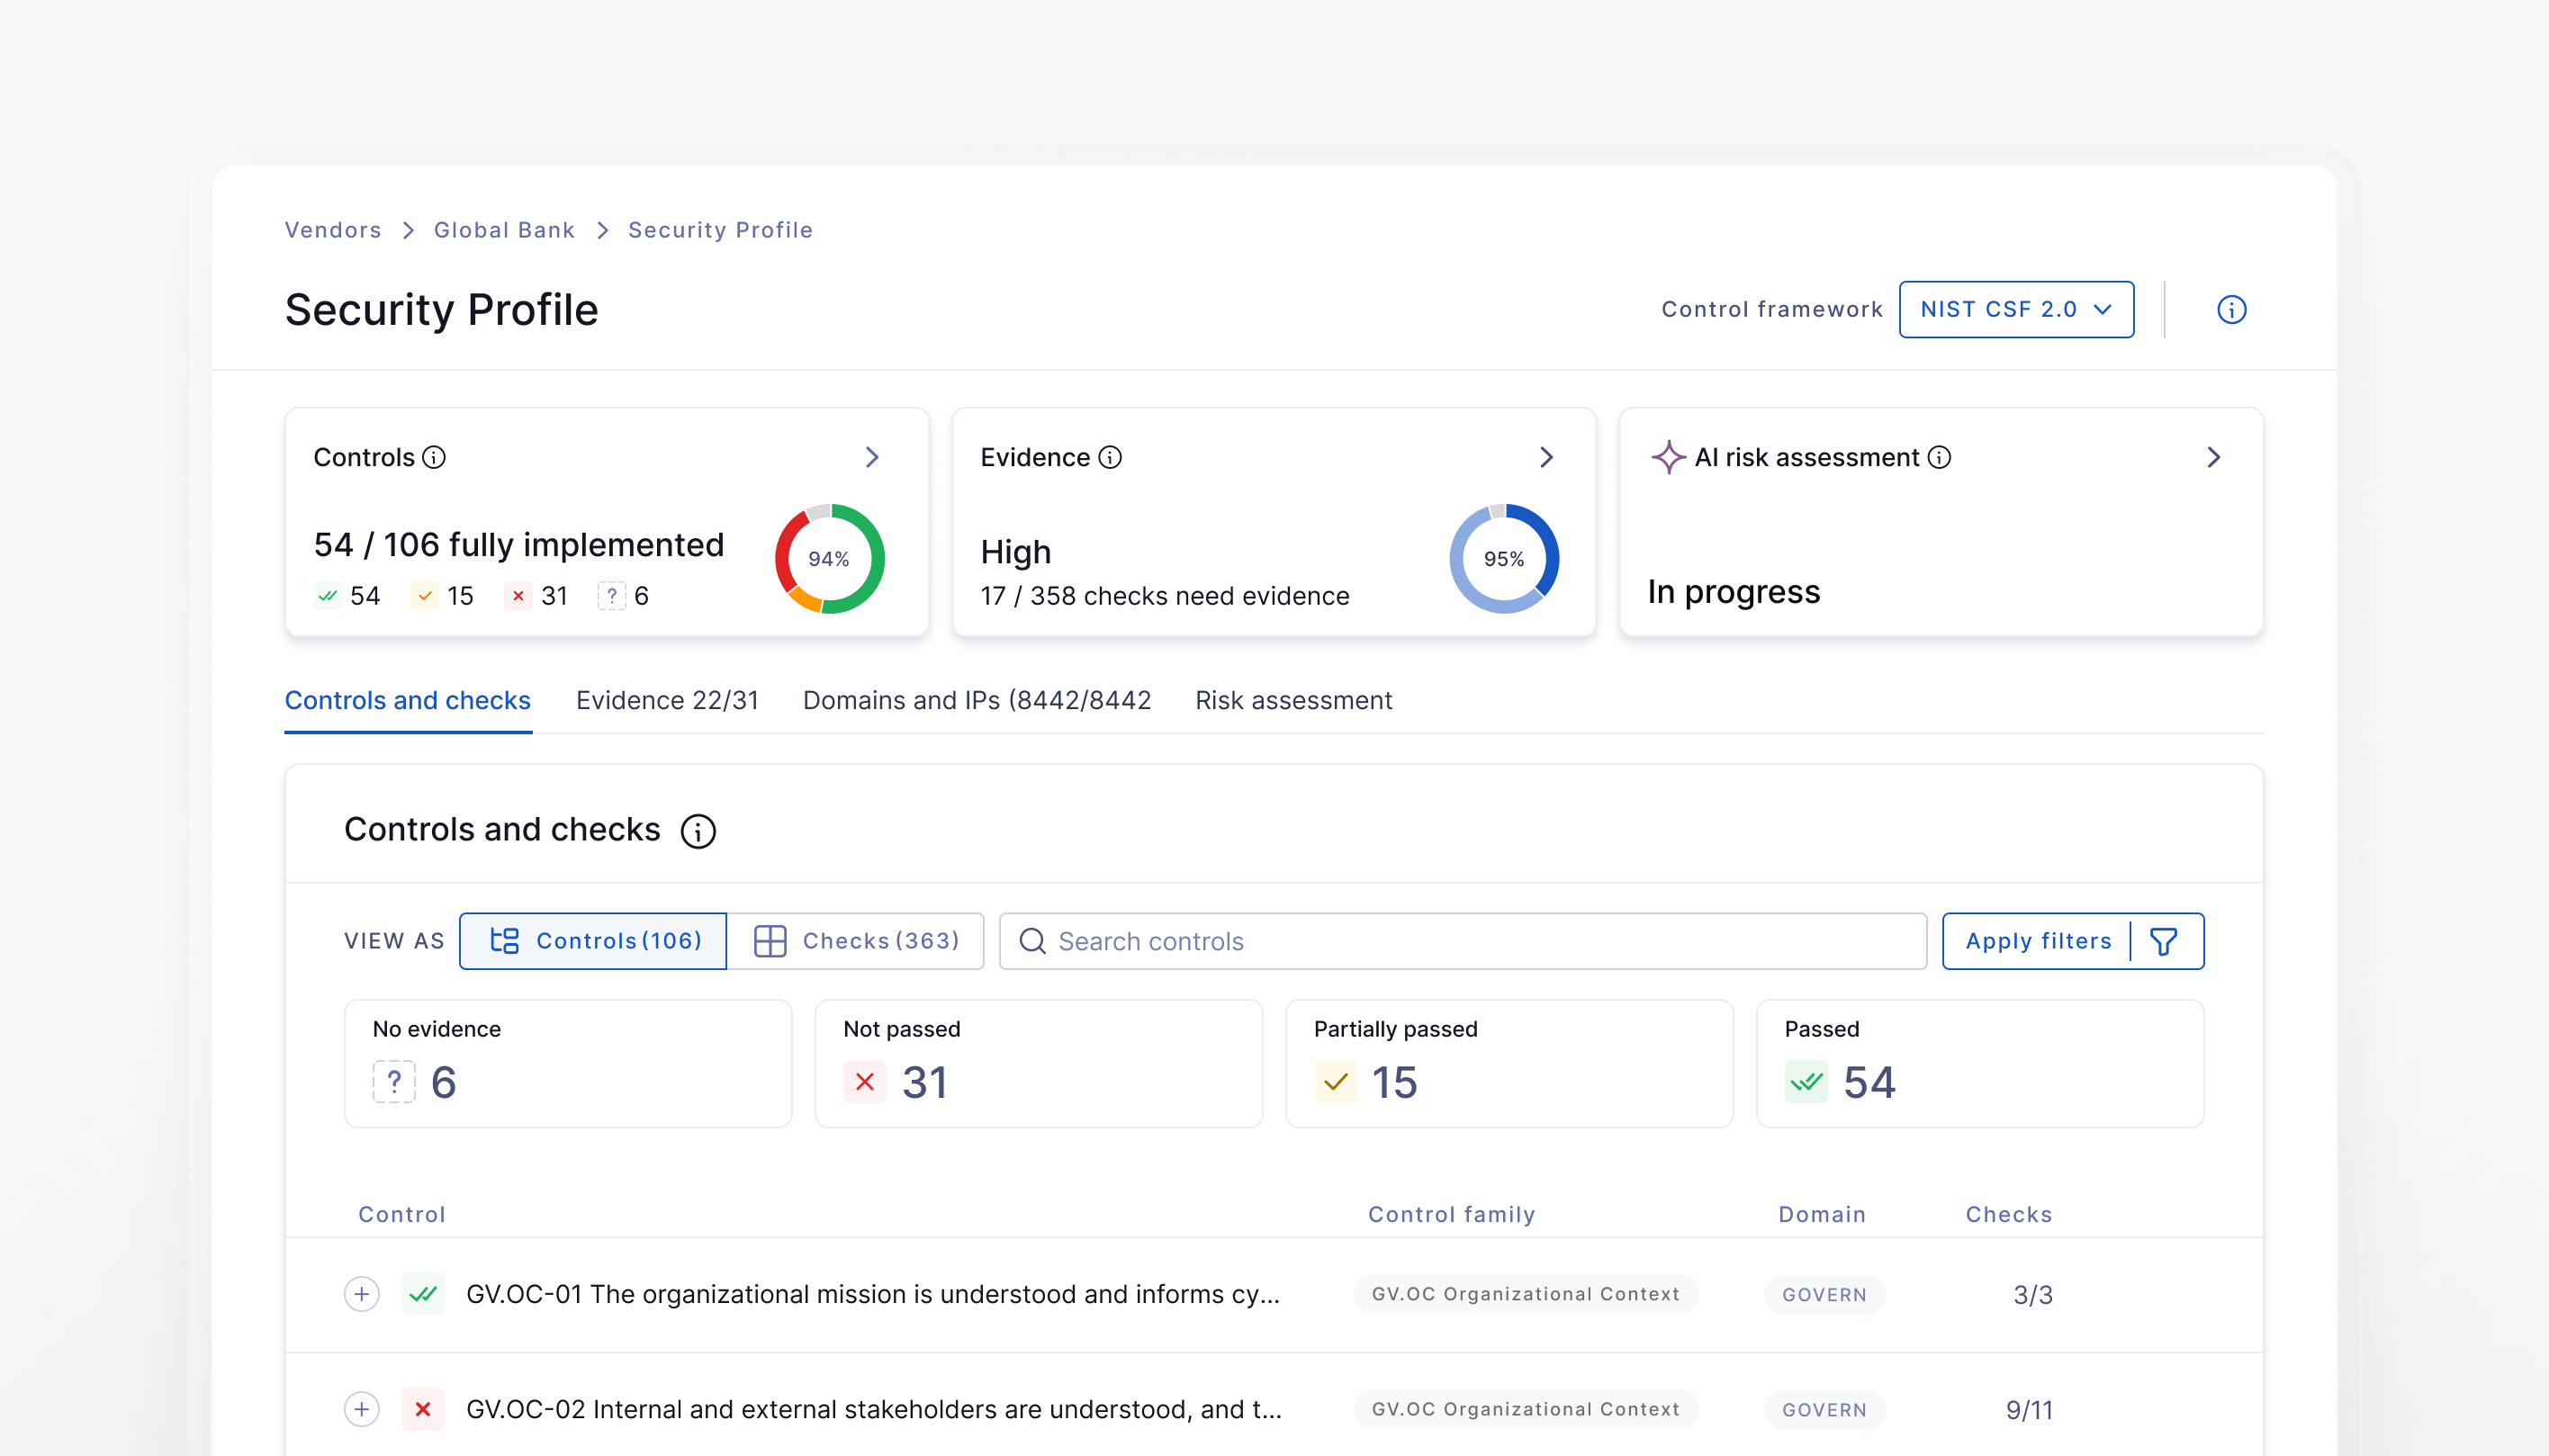
Mapping turns a critical or high tier into a defensible statement about control expectations and evidence. That framework mapping is what makes the model explainable when two vendors with similar spend receive different diligence.
Keep the map short enough that assessors can apply it, as a sprawling control catalog that nobody uses defeats framework alignment.
You can use Vendor Risk assessments with the same map. Tier-aligned templates and questionnaires stay tied to the frameworks you already run. Higher tiers then collect deeper evidence without a separate diligence process for every vendor.
Set vendor expectations by tier before the relationship hardens
Set expectations during onboarding and contracting, before an incident forces a frantic email thread. For each tier, define incident notification windows, reporting frequency, right-to-audit or evidence refresh cadence, security contact roles, subcontracting rules, and exit or transition assistance. Higher tiers need tighter terms and named owners on both sides.
Document backup plans for critical vendors, including alternate providers, data escrow, or manual workarounds where technology failover is limited. If continuity scored high in the model, the contract should reflect that dependency.
New data flows or regions should trigger review. Continuous monitoring of external posture and questionnaire drift keeps the tier from becoming a one-time onboarding artifact.
What tools help with vendor segmentation and tiering strategies?
The tools that help with vendor segmentation and tiering strategies are vendor risk management (VRM) platforms. These systems discover and onboard vendors, track reviews, assign tiers, and continuously monitor them.
Look for platforms that match each tier to different questionnaires, evidence requirements, and review cadence.
For segmentation methods and portfolio design, read our guide on reducing supply chain security risks with vendor segmentation.
How UpGuard Vendor Risk supports tier-aligned review
UpGuard Vendor Risk supports tier-aligned review by discovering and onboarding vendors, prioritizing them by criticality, and matching each tier to assessment templates so inherent-risk labels change review depth.
Security ratings refresh daily across every monitored vendor, and you can set custom alerts to fire when a score crosses a threshold you define, which is what turns a rating into a tier trigger.
Security Profile comes pre-mapped to ISO 27001:2022 and NIST CSF 2.0, with assessment templates covering NIST SP 800-53, CIS Controls, and CCM, so tier depth stays tied to the frameworks your program already reports against.
For a personalized walkthrough of how Vendor Risk supports tiering best practices, book a demo with our team.
Frequently asked questions
How to tier vendors by security risk?
Score data access (at least 40% weight), operational continuity, regulatory mandates, strategic exposure, and security resiliency. Apply a fixed cut-off to the weighted total. Raise the tier under a critical override when a vendor breaches any single hard threshold, and log the change.
What's the most efficient way to score and tier vendors by risk level?
Use one short weighted scorecard with data access at 40% or more, fixed tier bands, and critical overrides. Match each tier to review depth so two analysts reach the same result from fixed information. Automate intake and re-score triggers at scale without changing weights ad hoc.
What tools help with vendor segmentation and tiering strategies?
Choose a vendor risk management (VRM) platform that discovers and onboards vendors, tiers them, builds portfolios, applies labels, and supports custom attributes so segmentation and assessment depth stay aligned. Combine the platform with a clear segmentation method rather than treating software as the strategy.
Which tool supports multi-tier vendor security assessments?
Tools that support multi-tier assessments discover and onboard vendors, then attach different questionnaires, evidence requests, and monitoring cadence to each tier label. With UpGuard Vendor Risk, you can bind criticality and templates so the tier changes how deeply you review the vendor.
Related posts
The Evidence Is In: UpGuard Named a Leader in the IDC MarketScape for Worldwide Third-Party Risk Management
