Release notes
CISA known exploited vulnerabilities tags and notifications

Chris Schubert November 9, 2022
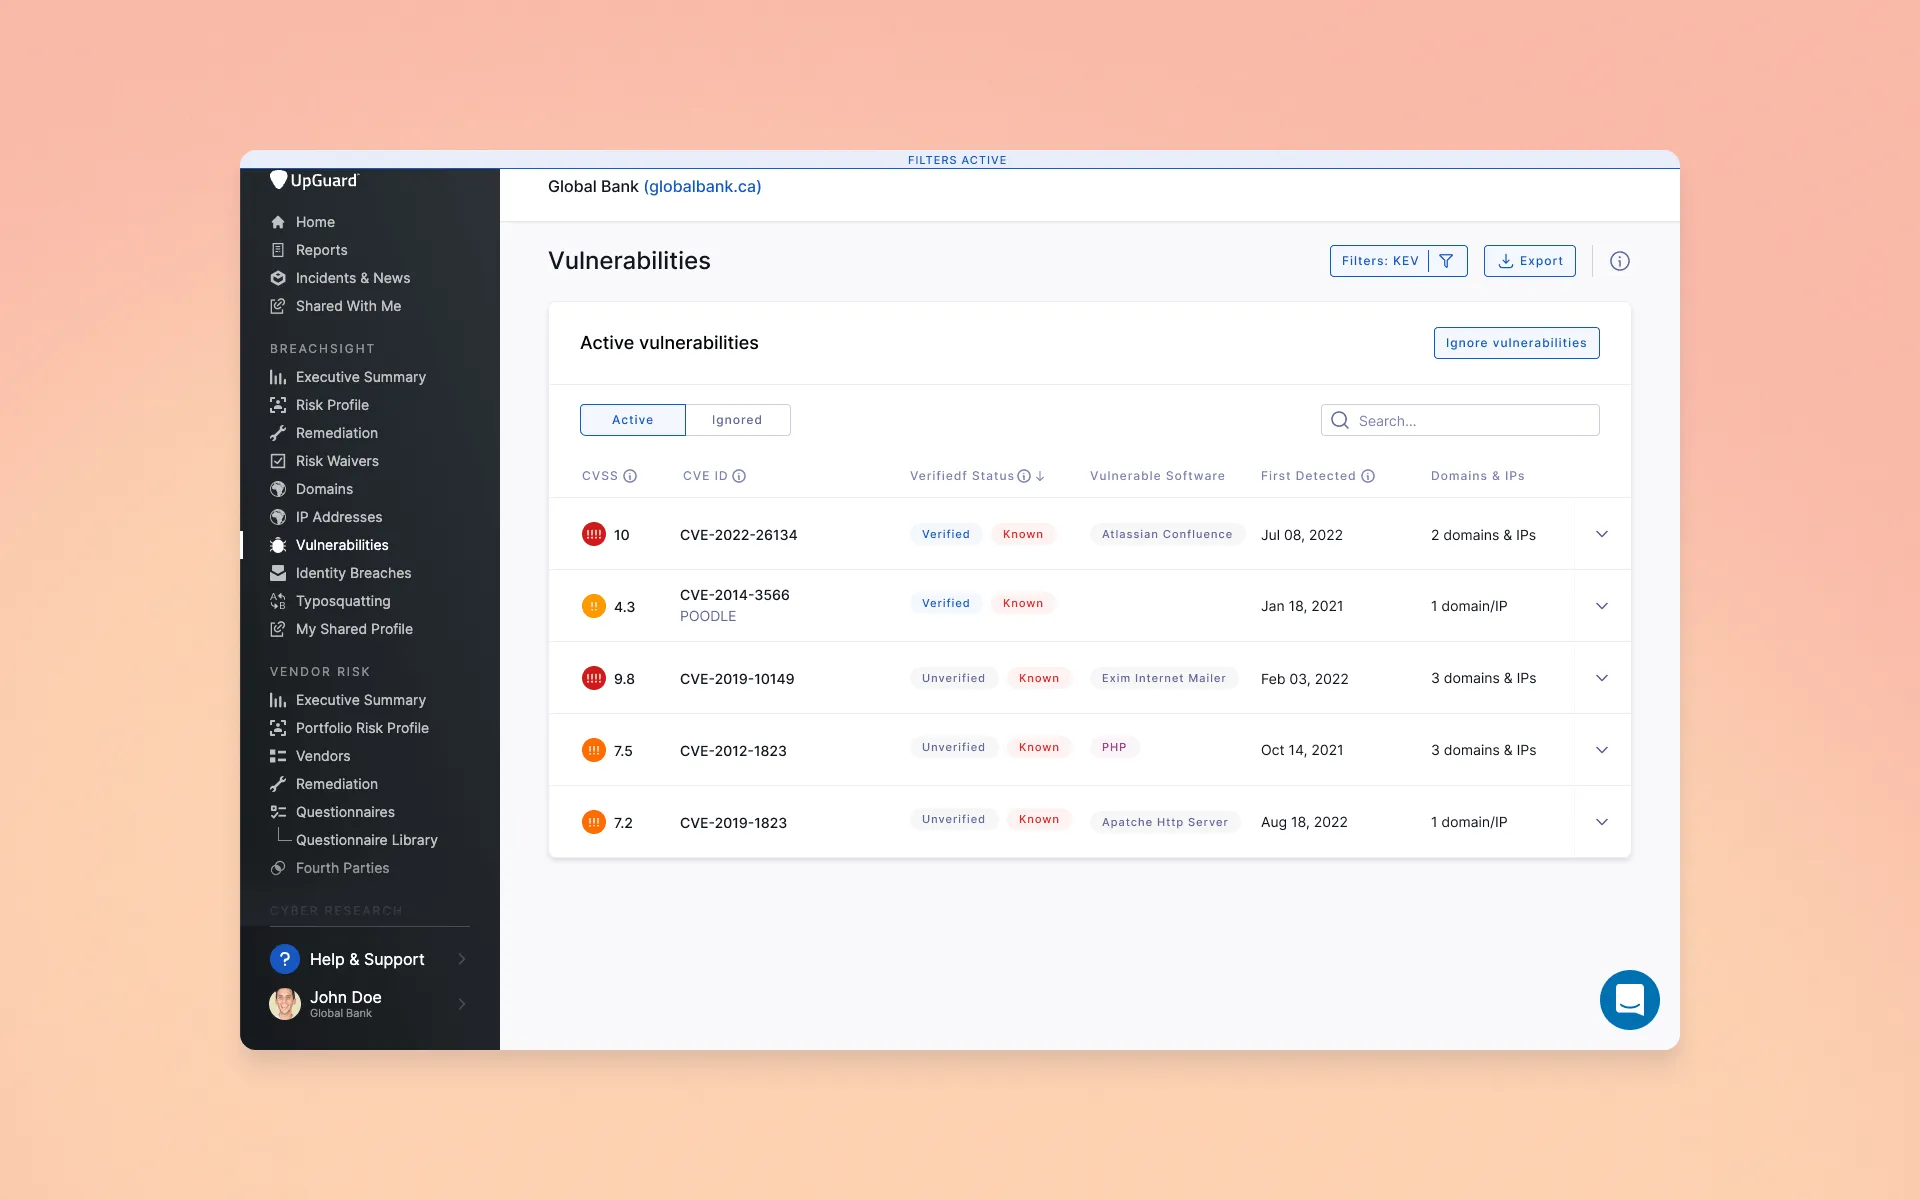
You can now quickly identify which vulnerabilities on your assets are on CISA’s list of known exploited vulnerabilities (KEV), pointing you towards your highest areas of risk at a glance.
At any given time, threat actors are only targeting a small number of vulnerabilities, and this feature will allow you to prioritize the remediation of those vulnerabilities that directly impact your business. As part of this feature, you can also set up notifications to be informed when a vulnerability you have is added to the KEV list.
The new Data Leaks Home page provides more reporting capabilities for understanding where those mentions of your brand keywords are occurring. UpGuard’s Data Leaks engine processes billions of files each day to identify the small number of sensitive data exposures affecting our customers. This information will help understand your risk profile for leaks and demonstrate your controls for the timely detection of data exposures. Over the coming weeks, this feature will be rolled out to accounts with Data Leaks enabled.
We’ve added detection for more risks related to website security headers. These risks will be released in a “provisional state,” meaning they are visible but do not affect scoring. After a provisional period of one month, the risks will be updated to include scoring penalties.
We’ve added new capabilities to the remediation export to assist with tracking and auditing of remediation activity, including:
To learn more about these improvements check out How to export your internal remediation requests and How to export your vendor remediation requests.


