Release notes
Easily convert documents to additional evidence

Annie Luu August 30, 2023
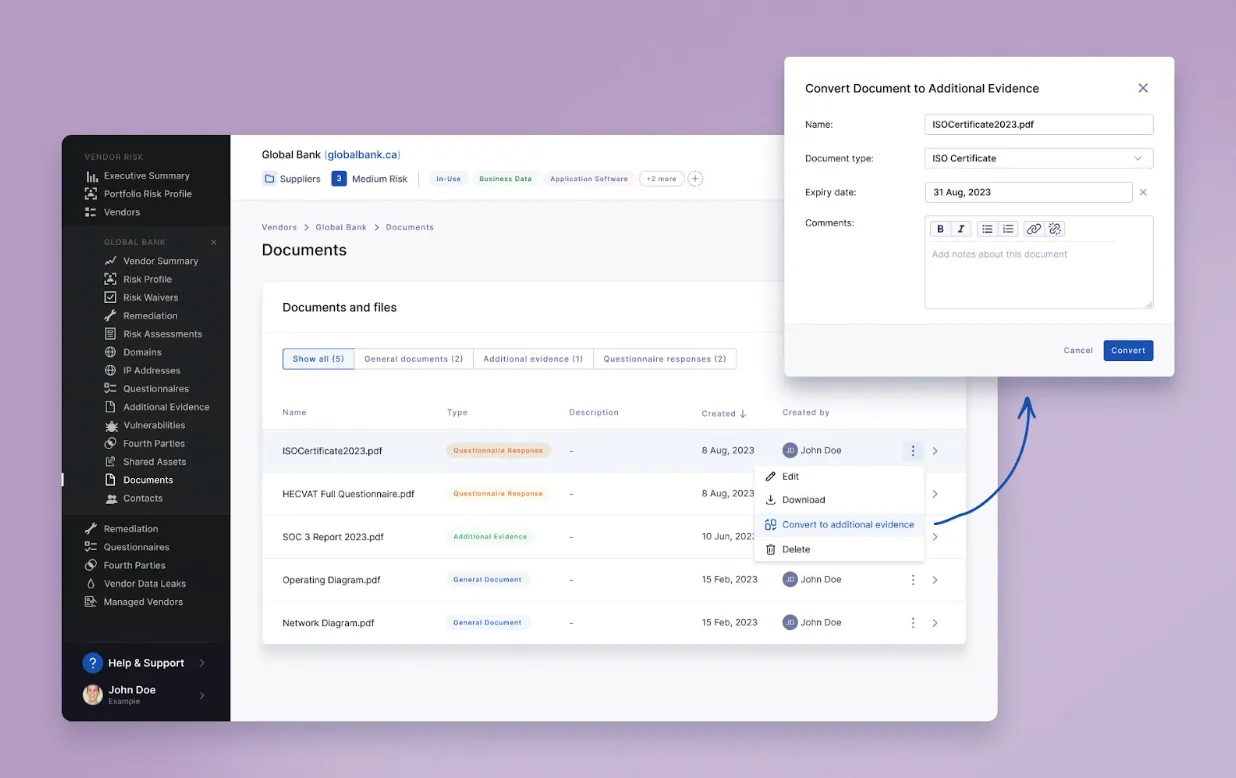
We’ve made it easier for you to convert documents included with questionnaires and general documents into additional evidence. This allows you to easily classify and add risks to these documents, and use them as part of your vendor risk assessments. To learn more see How to capture additional evidence.
Citrix ShareFile has been targeted by attackers to exploit CVE-2023-24489. We now identify which sites are running ShareFile so you can ensure they have been updated to the current version. We also identify sites using the Ninja Forms WordPress plugin, which is being targeted via CVE-2023-37979, CVE-2023-38386, and CVE-2023-3839.
Our JavaScript vulnerability detection has been extended to include Bootstrap, Chart.js, Handlebars, and many other popular libraries to ensure that websites you depend on aren’t affected by frontend vulnerabilities.


