Upload it once.
Reuse it everywhere.

Keep every SOC 2 report, policy, and questionnaire answer in one central repository, then pull approved documentation straight into your Trust Center and future sales questionnaires.

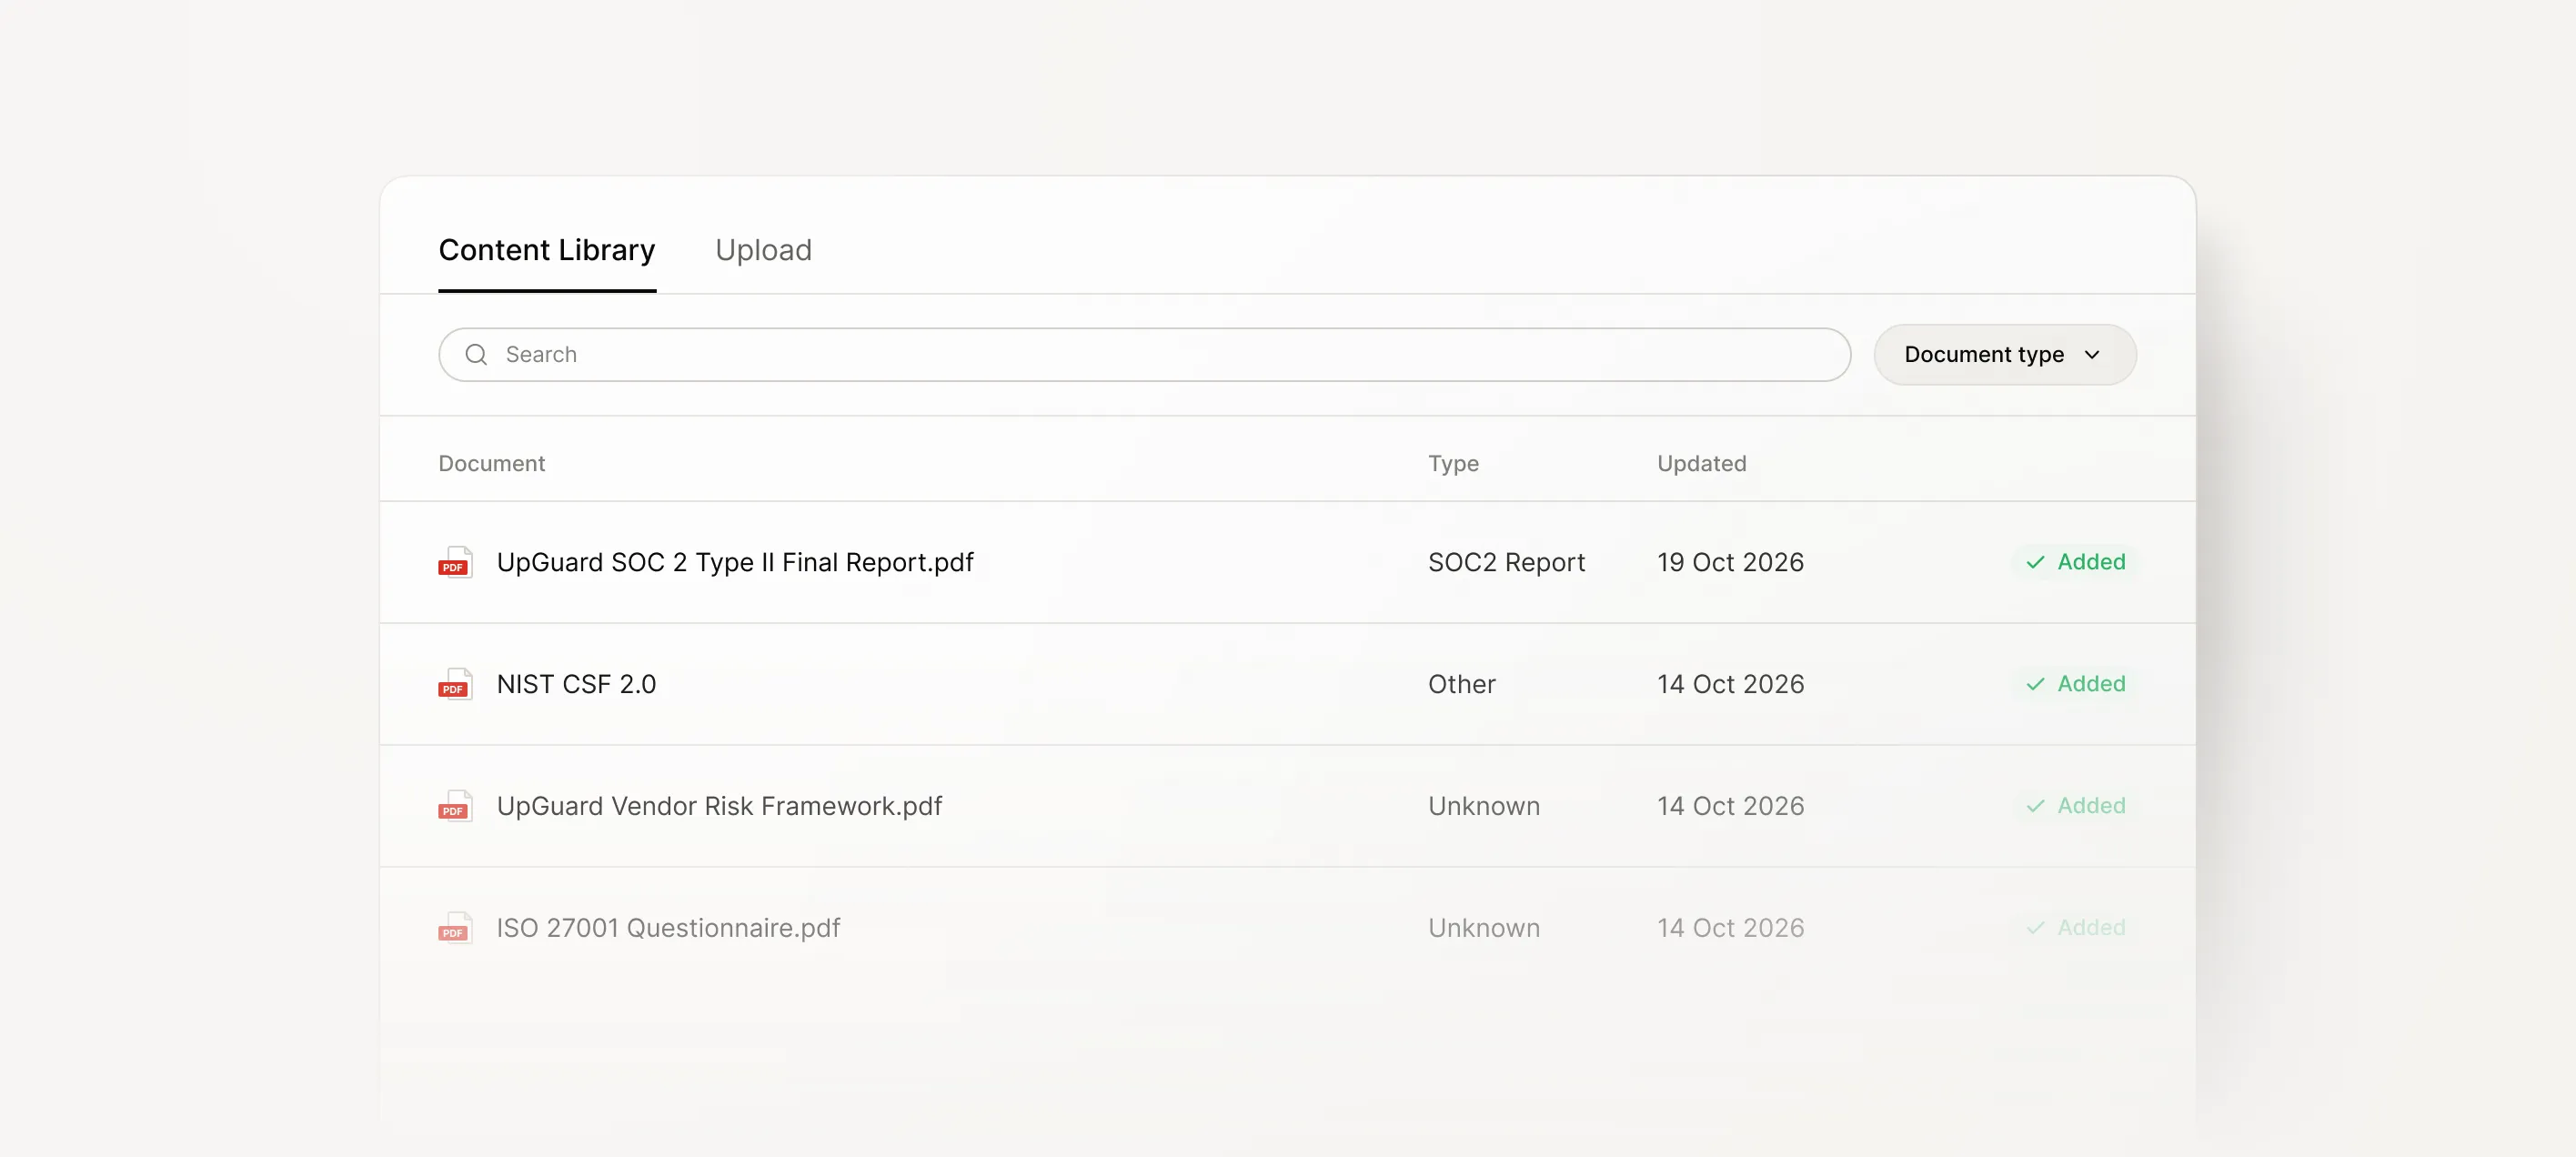
Content Library listing a SOC 2 report, NIST CSF 2.0 and other documents with their type, last updated date and status

Your team is constantly searching for updated SOC 2 reports, pen tests, and policy documents for each new prospect. But that documentation already exists. You need an organized workspace that turns static compliance files into reusable sales assets across every customer touchpoint.

One library, every document

The Trust Exchange Content Library gives you a single home for all your security evidence, so you never have to start from scratch.

  • Centralize every report: Store your ISO 27001 certifications, SOC 2 reports, information security policies, and penetration test results in one location.
  • Import past evidence: Review and pull in documents you’ve already uploaded to past questionnaires so you aren’t starting from zero.
  • Maintain version history: Keep your library clean by uploading new document versions over time instead of creating duplicate files.
  • Track document expiry: Monitor certificate and document expiration dates so your team gets notified before materials go stale.
Uploading an ISO 27001 document with a name, type and access protection turned on

Reuse it, don’t re-upload it

Stop missing sales deadlines to clunky deal workflows.

  • Publish with a click: Push any library document straight to your Trust Center using a simple access toggle.
  • Attach directly to questionnaires: Pull library files straight into active questionnaire responses instead of wasting time searching for them.
  • Maintain clear user roles: Full-access team members can save new files to the shared library, while read-only users can attach existing files to questionnaires without cluttering the repository.
  • Inspect document history: Review version histories, internal notes, descriptions, and deal usage history from a single properties panel.
A questionnaire question suggesting a SOC 2 report and ISO 27001 document from the library to attach

Layered protection built for control and compliance

  • Access protection travels with the document: Turn file-level protection on or off per item, independent of where it’s published. Enforce gatekeeping, custom NDA signatures, and dynamic PDF watermarks before buyers view sensitive files.
  • Track access with full audit trails: Complete access logs record exactly who requested, viewed, or downloaded each document, giving your legal and compliance teams complete visibility.
  • A living compliance record: Version history and expiration tracking ensure your library always reflects your current security posture — not last year’s.
Document properties for a SOC 2 report showing its type, the Trust Centers it is shared on, and access protection turned on

Save time and streamline your trust management process