Release notes
PHP2Shell detection now live in UpGuard

Mark Barber October 21, 2026
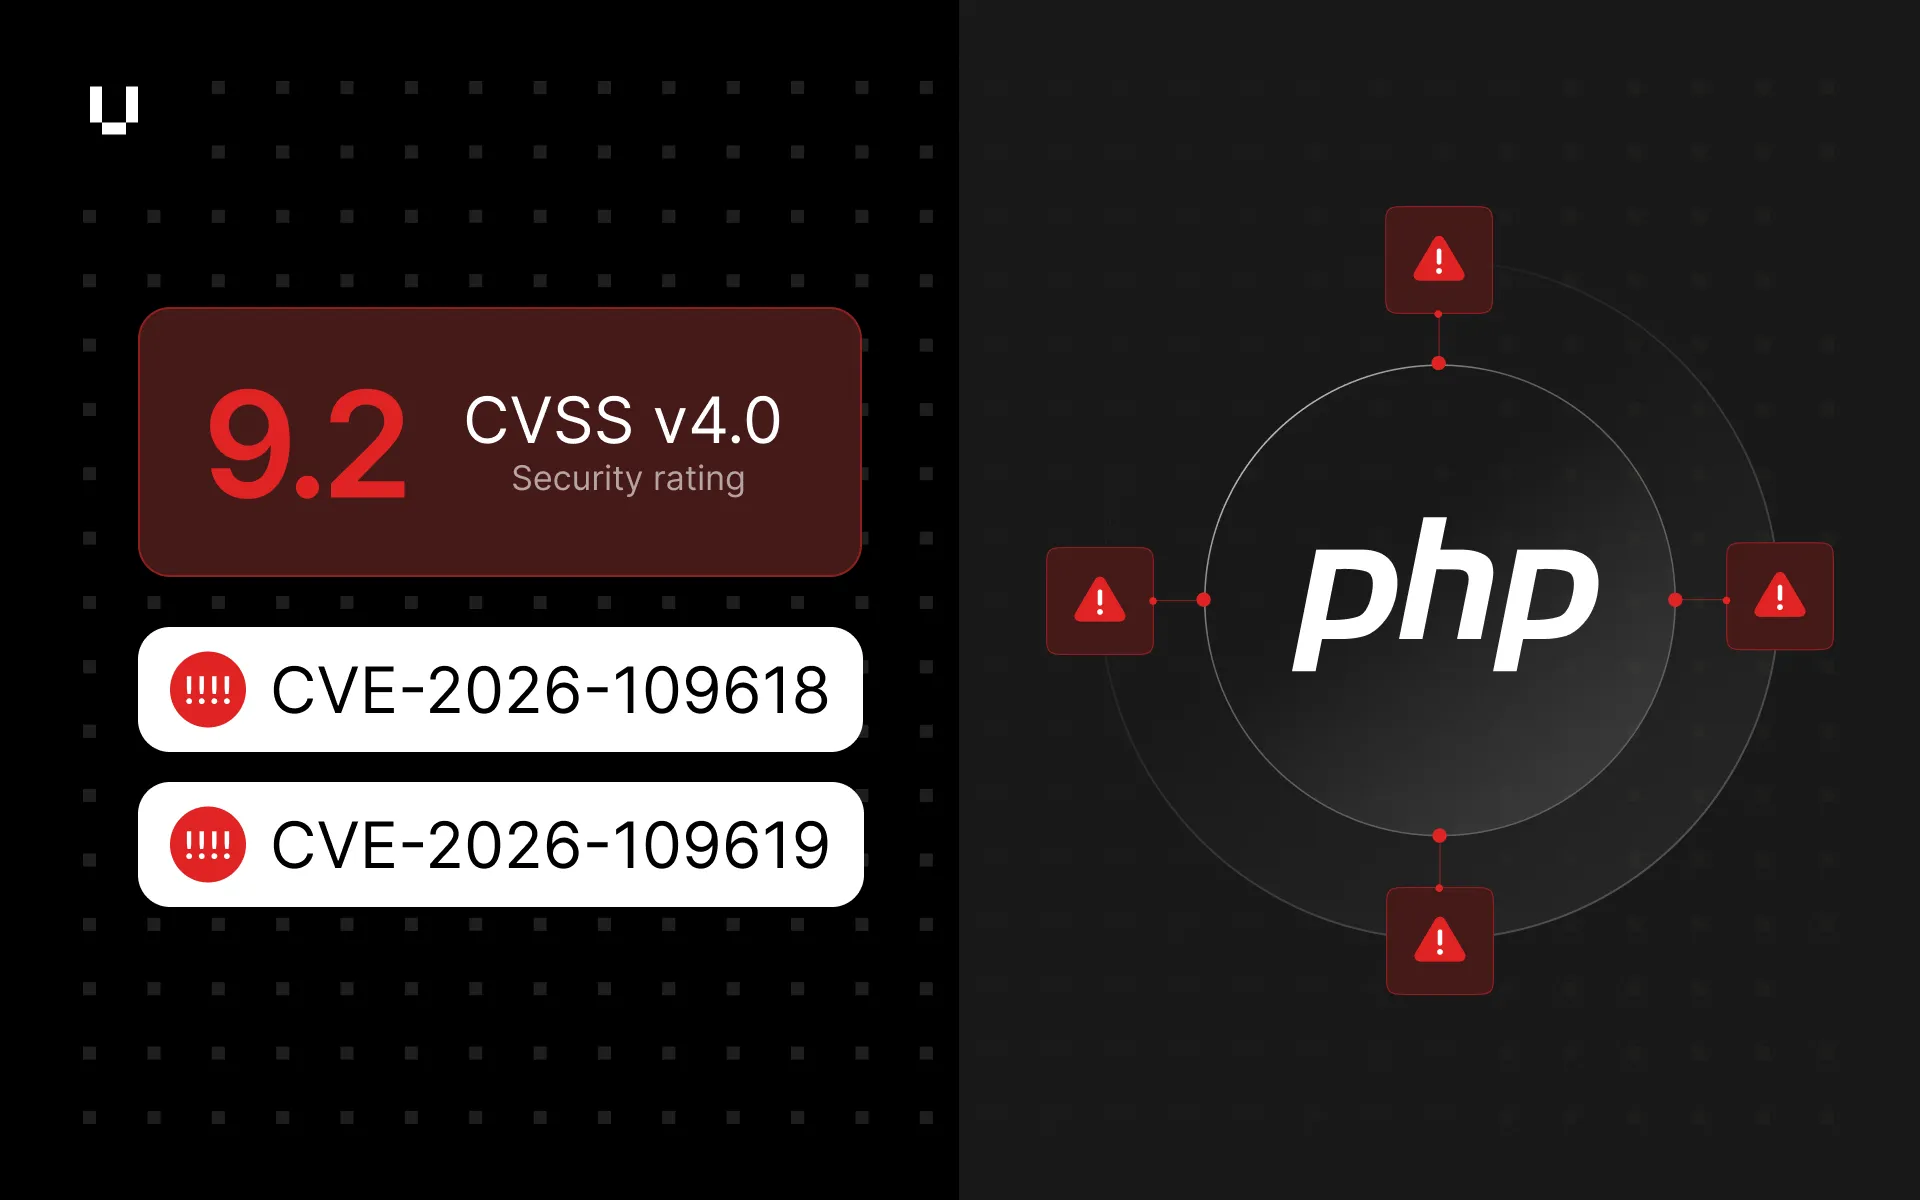
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP vulnerabilities disclosed this week. They let an unauthenticated attacker run code on a vulnerable web server. The real concern is how far back they go. Every version from PHP 5.4.0, released in 2012, up to 8.2.34 is affected, along with 8.3.0 to 8.3.35, 8.4.0 to 8.4.26 and 8.5.0 to 8.5.11. Fixes are available in 8.2.35, 8.3.36, 8.4.27 and 8.5.12. PHP 5.x, 7.x, 8.0 and 8.1 are end-of-life and won’t get a fix, so anything still running those versions needs a major upgrade. Workarounds are circulating, however official advice from PHP is that upgrading is the only reliable fix.
UpGuard has added both CVEs as verified vulnerabilities in Breach Risk and Vendor Risk. Detection is based on the PHP version, so any domain or IP running an affected version gets flagged. Security teams can see where their organization and their vendors are potentially exposed and prioritize patching and remediation requests.