Release notes
Close related exposed credential threats in one step

Mark Barber October 20, 2026
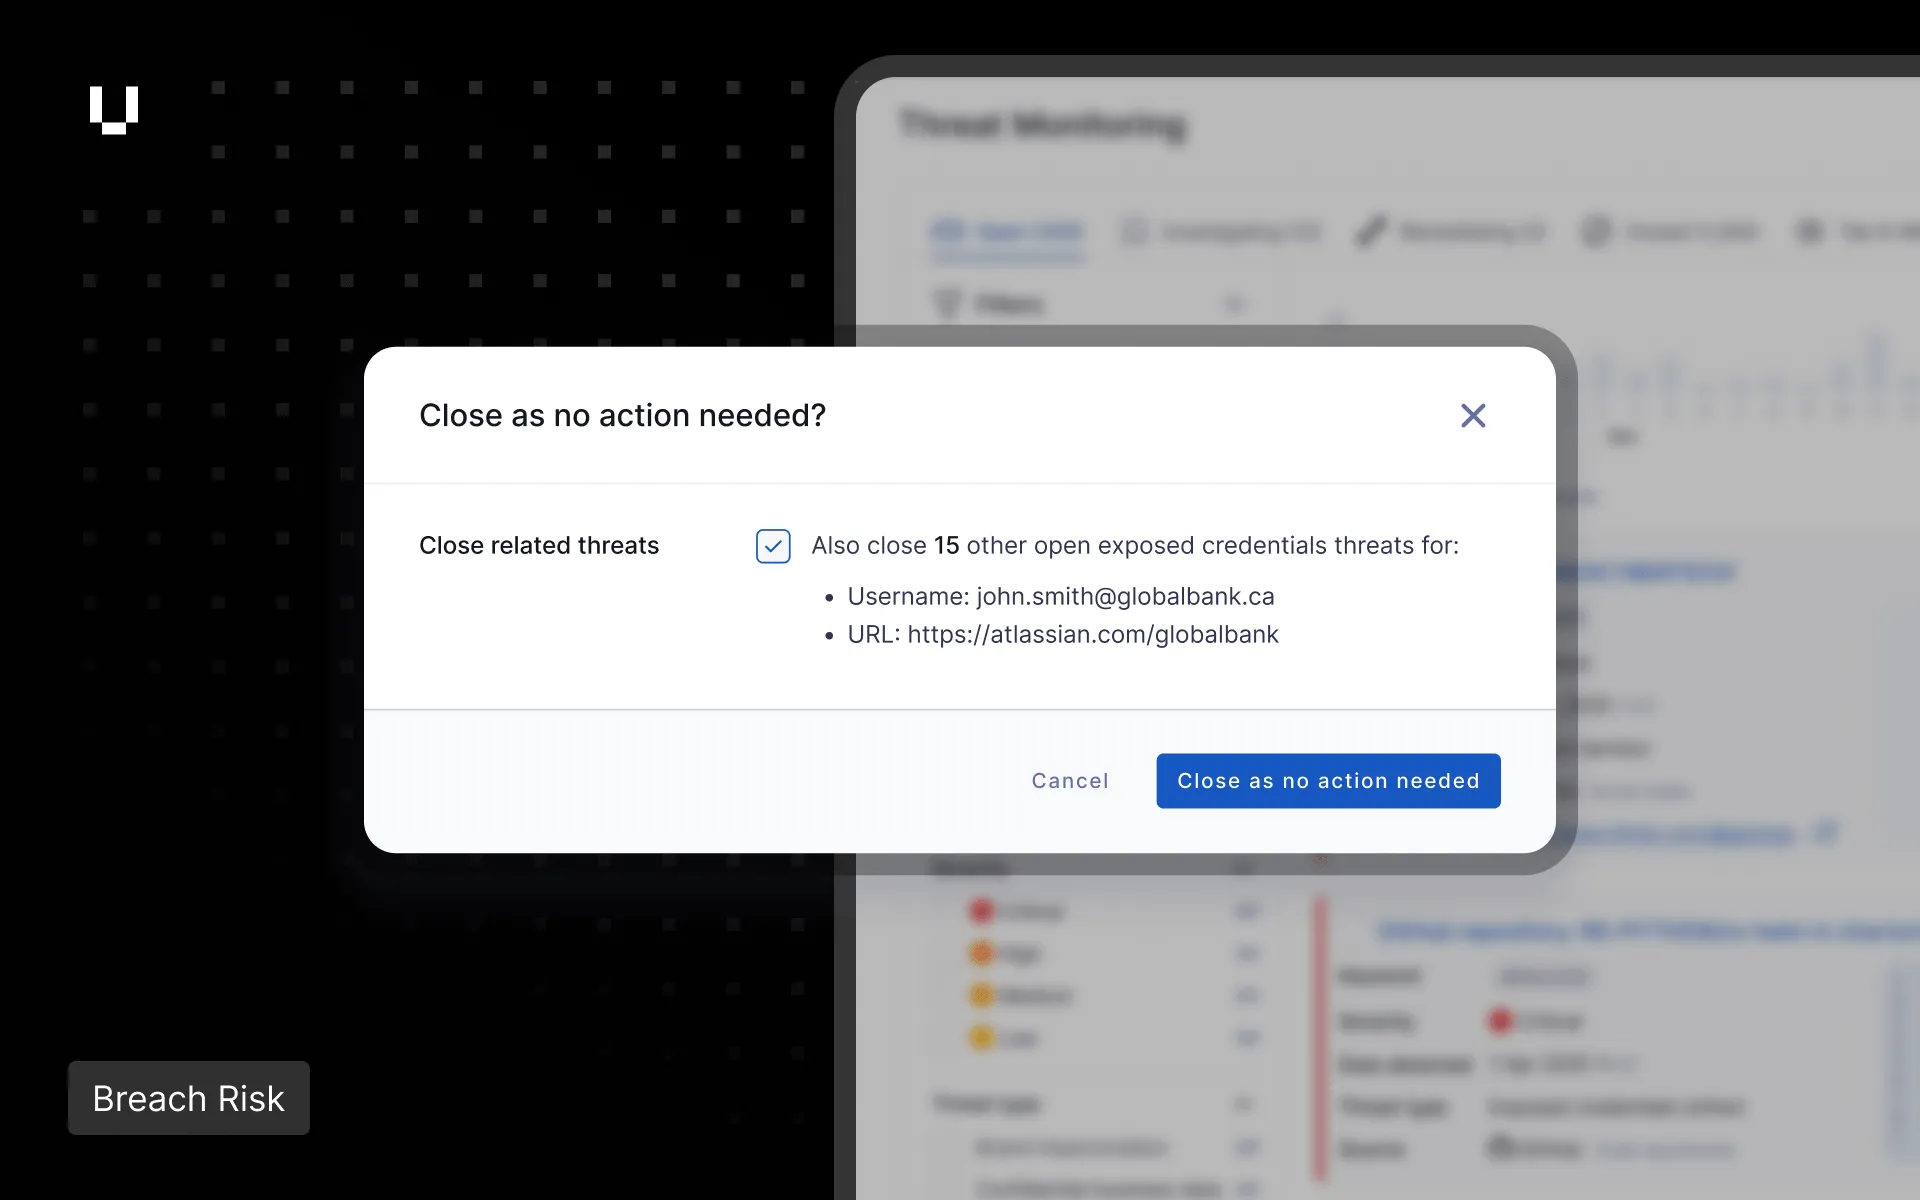
When users mark an exposed credential threat in Threat Monitoring as Remediated or No action needed, they can now close every other open exposed credential threat for the same username and URL at the same time. This removes the need to work through duplicate detections one by one, so the queue stays focused on threats that still need attention.