Release notes

Ability to shortlist key risks in risk assessments

Annie Luu November 22, 2023
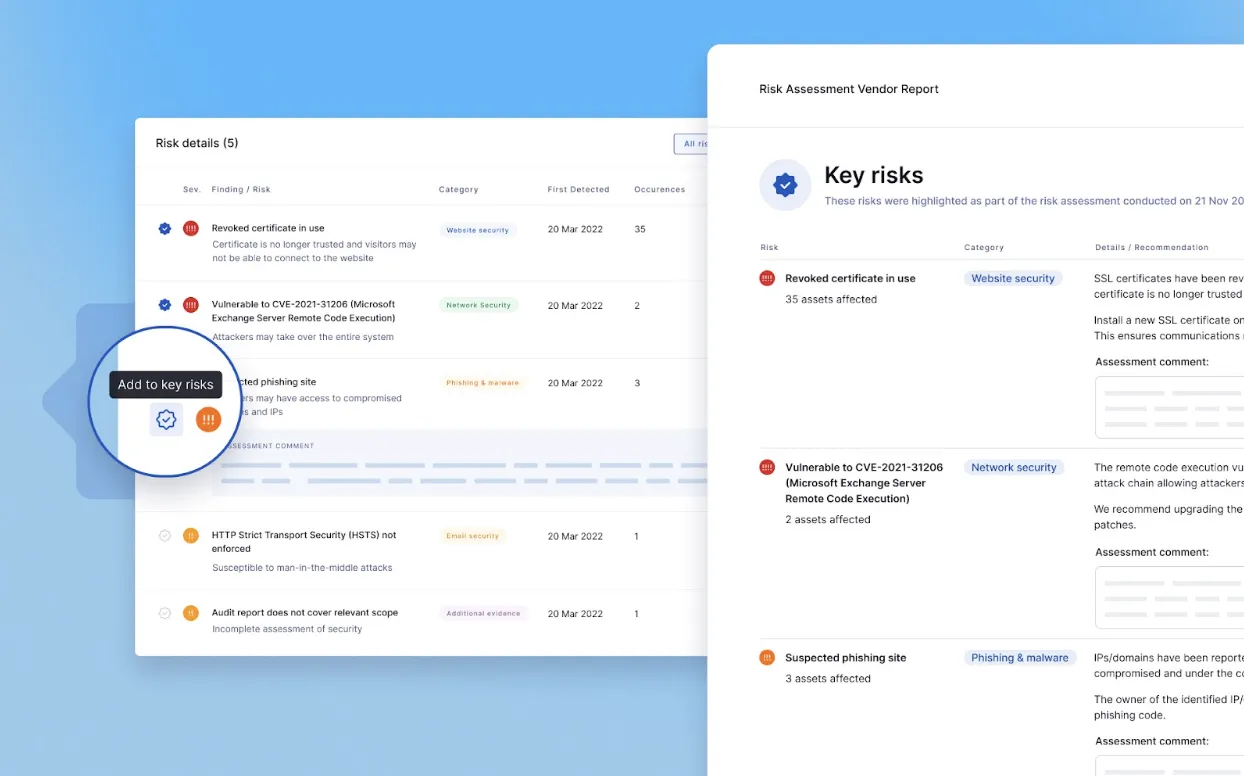
We’ve added the ability to create a shortlist of key risks as part of a risk assessment, allowing you to highlight important risks and those requiring follow-up. You can choose to include only key risks as part of your risk assessment report, in lieu of displaying the full list of risks. To learn more see How to complete a risk assessment.

API flexible permissions

We’ve revised API permissions to allow a finer-grained set of permissions and visibility:

  • Added a Read/Read&Write flag to allow a given API key to only access GET functions or to be able to access GET/PUT/POST and DELETE functions.
  • Expanded on the current Data Leaks permission to allow an API key to be defined by role.
  • To protect existing integrations all existing API Keys will be granted full access. The new model will only relate to keys generated after this release.

To learn more see UpGuard’s API documentation.

Vendor monitoring API changes

We’ve created specific API endpoints to start monitoring and stop monitoring a vendor. This allows us to follow more established and consistent API design practices as well as restrict the monitoring to only those API Keys that have Vendor Risk Read&Write permissions. In subsequent releases, we will deprecate the “start_monitoring” flag in the /vendor API endpoint and remove that feature:

  • Vendor ID or Primary Host Name) to the list of monitored vendors. This supports the same functionality as our existing /vendor API when start_monitoring = true, such as:

- The ability to apply labels and tiers;

- A wait for a scan feature that scans the vendor before returning the results;

- Checks on UpGuard licenses maximum Vendor counts.

  • /vendor/unmonitor – A new endpoint that will remove the specific vendor (based on Vendor ID or Primary Host Name) from the list of monitored vendors.

To learn more see UpGuard’s API documentation.

SysAid vulnerability detection

We’ve added detection for the SysAid product, its version, and associated vulnerabilities, notably CVE-2023-47246 being exploited by the Clop group.

Other improvements

  • This release includes a number of bug fixes.
View all release notes

UpGuard Release Notes

Learn about new features, changes, and improvements to UpGuard.

Clearer citations and timeline for Security Profile checks

Mark Barber August 26, 2026
Read more

Subprocessors in Trust Center

Mark Barber August 12, 2026
Read more

Cloud and core infrastructure frameworks in Security Profile

Mark Barber July 29, 2026
Read more

Complete questionnaires without closing remediation

Mark Barber July 15, 2026
Read more

Company name aliases for smarter detection

Mark Barber July 1, 2026
Read more

FortiBleed Exposure Detection

Mark Barber June 25, 2026
Read more

Updated application usage policy controls

Mark Barber June 17, 2026
Read more

New threat signal: Published MCP server definitions

Mark Barber June 3, 2026
Read more
View all release notes

See UpGuard In Action

Book a free, personalized onboarding call with one of our cybersecurity experts.
Free instant security score

How secure is your organization?

Request a free cybersecurity report to discover key risks on your website, email, network, and brand.
Website Security scan results table Cyber security rating score 850 out of 950