Release notes
Fortra GoAnywhere MFT CVE-2024-0204 detection added

Annie Luu January 30, 2024
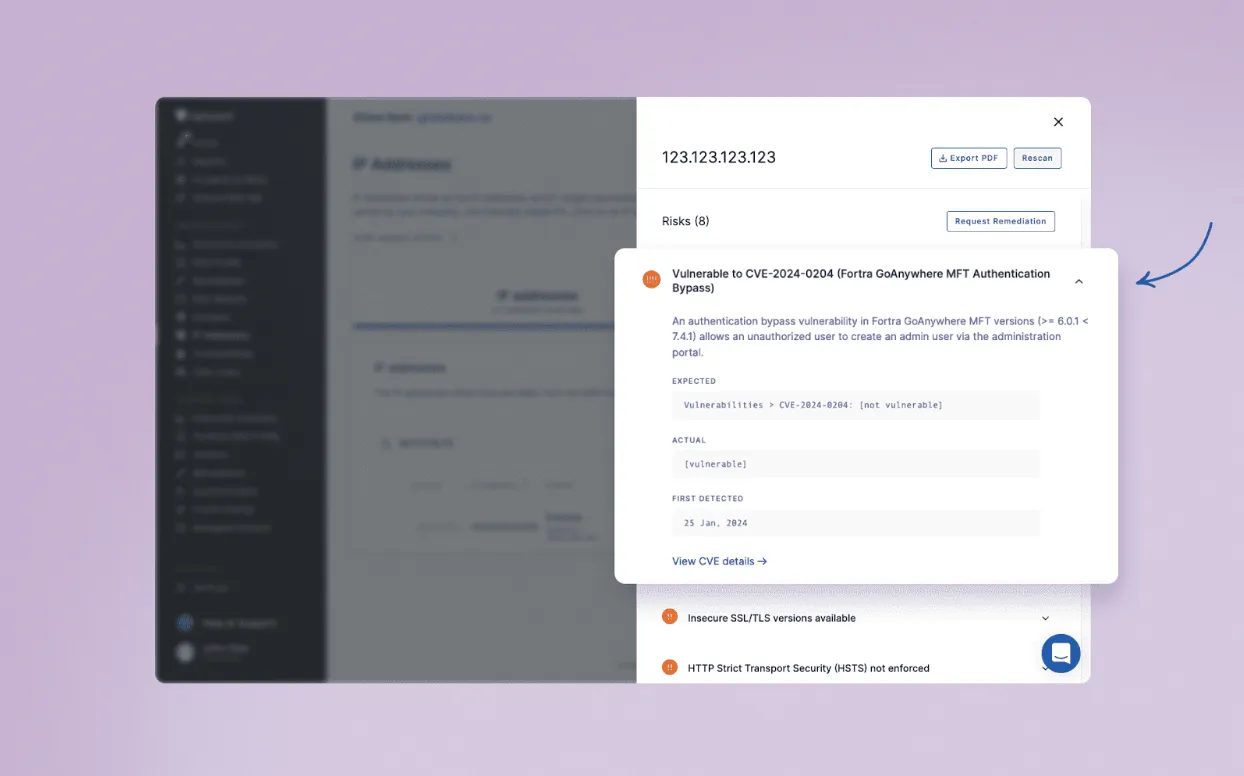
CVE-2024-0204, a critical authentication bypass vulnerability in Fortra’s GoAnywhere Managed File Transfer (MFT) software, allows unauthorized users to create admin users and bypass authentication requirements.
While this vulnerability is not yet in the Known Exploited Vulnerabilities catalog, GoAnywhere was previously targeted by the Cl0p ransomware group in early 2023, making it crucial to patch now before it’s too late.