Release notes
Introducing Multiple Trust Pages per UpGuard account

Mark Barber December 3, 2025
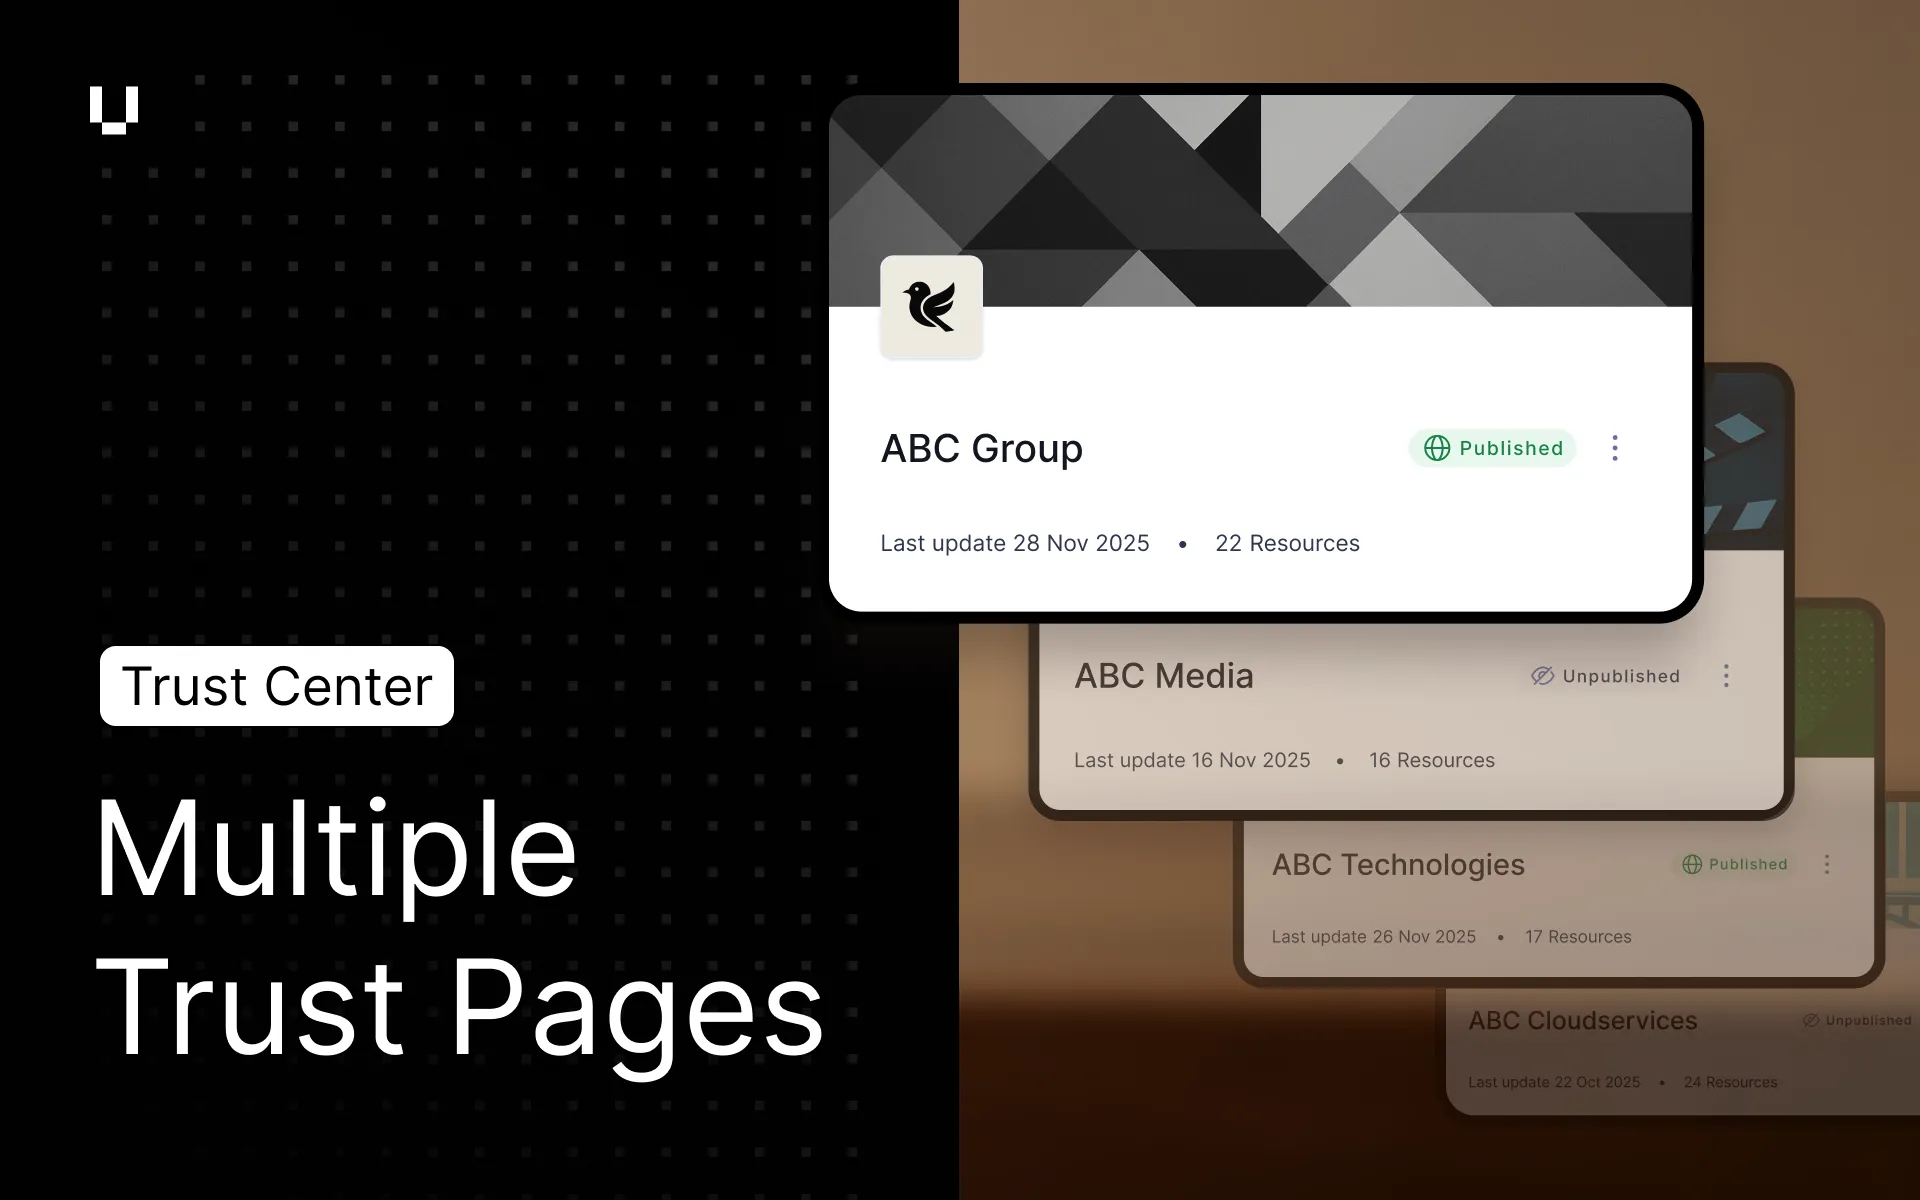
We have introduced the ability to create, duplicate, manage and publish distinct and customizable Trust Pages, each targeted to a specific product or acquisition. Users can apply custom branding and messaging to each of the Trust Pages to publish the security posture of their different products, ensuring that each product’s unique risk profile and compliance story is accurately and professionally conveyed to its specific audience. Users can also easily set up independent Trust Pages for child companies following an acquisition, ensuring each child entity maintains its security profile and unique brand identity.
Multiple Trust Pages expands the range of supported use cases, giving users greater flexibility in how they present and manage their security narrative.
We have added support for product and version detection of both PaperCut NG and PaperCut MF - a commonly used print server in enterprises. Both of these PaperCut products are often exposed on the internet and have high severity vulnerabilities associated with them that are known to be exploited by threat actors. This improvement gains visibility into the product and version running.
Our vibe coding monitoring has been expanded to include support for Streamlit.io as a new source of vibe-coded threats. This enhances our ability to detect impersonation attempts, leaked credentials, and accidental disclosures caused by modern AI-assisted coding platforms.
Identity-theft detection has been expanded to include signals from credential-dump sources such as combolists, paste-site publications and other aggregated data leaks where exposed credentials or login pairs appear publicly. As part of this update, customers can now choose how passwords are captured from these sources, selecting between redacted or plain-text collection, or no password collection at all (recommended), based on their security and compliance needs.
We have added a specialized Model Context Protocol (MCP) Server Security Questionnaire to help you assess the unique risks of AI agents connected to third-party tools. This assessment goes beyond standard API security to cover critical agentic threats, including Indirect Prompt Injection, excessive permissions, and supply chain integrity.
Users can now display CMMC (Cybersecurity Maturity Model Certification) Level1/2/3 badges on their Trust Pages to demonstrate targeted compliance and credibility. These badges are available to use under Trust Pages > “Security and Compliance” section.


