Release notes

Questionnaire changes view

Annie Luu November 24, 2022
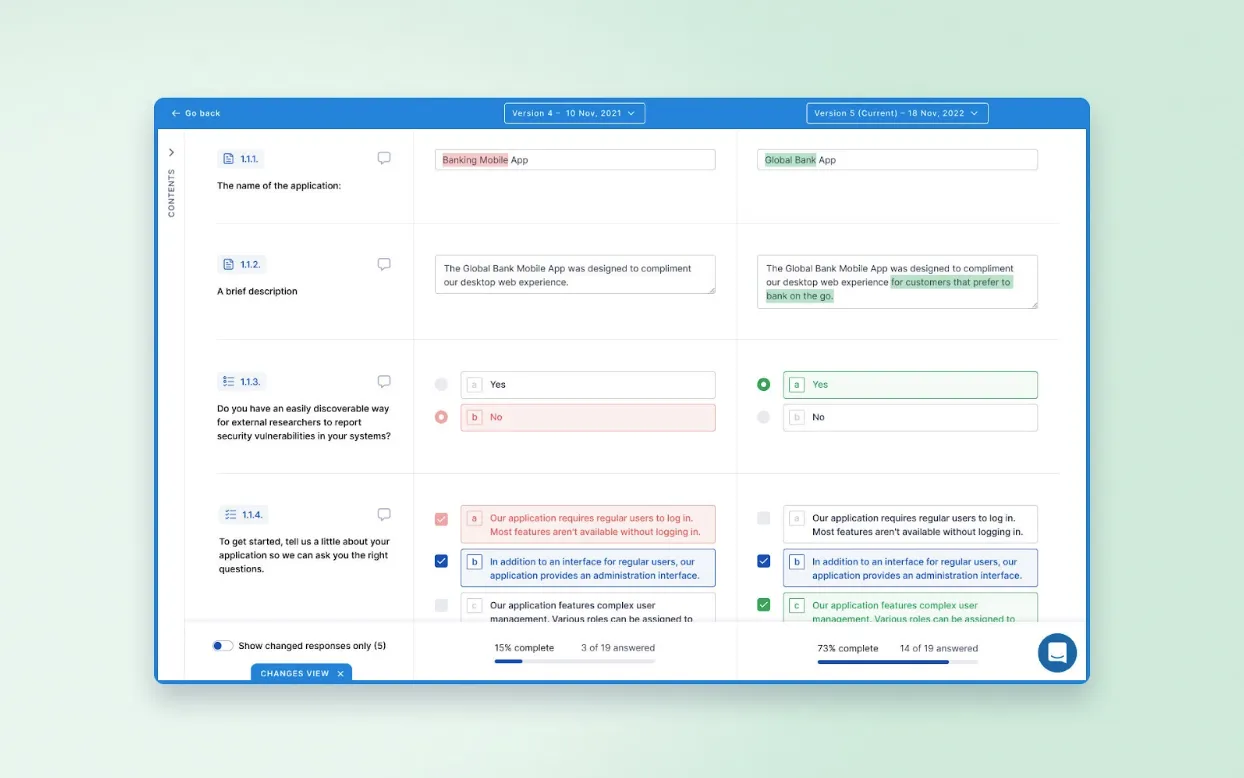
We are rolling out ‘questionnaire changes view’ to our Beta program customers. This feature enables you to compare responses between two versions of a questionnaire side by side, making it significantly faster and easier for you to re-assess your vendors.

The questionnaire changes view allows you to focus in on the responses that have changed. It gives you a more accurate and up-to-date picture of the vendor’s security posture without the risk of having answers that have changed without your knowledge. To learn more about using the changes view, this article has more information.

We are initially releasing the questionnaire changes view to a group of Beta customers. If you would like to be part of the Beta, please reach out to your Customer Success representative or send a request on Intercom.

Part of the Beta group and have feedback to leave? Share your thoughts here.

Notifications for risk reassessment and due dates

We’ve added some new notifications to help keep track of and follow up on your activity within UpGuard including risk reassessment dates, remediation request and questionnaire due dates.

You can configure these notifications to appear in-app on your home screen and/or via email in Settings. Email notifications will be switched off by default. To learn more check out Notifications in UpGuard.

Inviting a vendor to a free trial

We previously enabled UpGuard Vendor Risk customers to provide 14 days of free access to their vendors. We’ve improved this feature by making the invite button more visible in the platform—this can be found in any vendor’s header next to the vendor name.

Learn more about how you can proactively improve your third party security by providing your vendors access to the UpGuard platform here.

Addition of new HECVAT questionnaires

We’ve added two new questionnaires to the library—the Higher Education Community Vendor Assessment Tool (HECVAT) questionnaire, as well as a HECVAT Lite version—which will help institutions align their vendor risk posture to higher education-specific security controls.

Other improvements

  • Added informational risks to identify unmaintained assets, like those serving default server pages and web directories.
  • Added informational risks for sites without Certificate Authority Authorization records.
  • Data leaks where the developer’s business email address is found in the event history will be broken out into a “Github User” source. Keyword matches that occur in the code contents will continue to be labeled with the “Github” source.
  • Improvements to the performance of notifications. This includes batching a variety of notification types to reduce spam.
  • Improvements to the vendor search experience when used in combination with filters and portfolios.
  • This release includes a number of bug fixes.
View all release notes

UpGuard Release Notes

Learn about new features, changes, and improvements to UpGuard.

Brand impersonation detection across mobile app stores

Mark Barber September 9, 2026
Read more

Clearer citations and timeline for Security Profile checks

Mark Barber August 26, 2026
Read more

Subprocessors in Trust Center

Mark Barber August 12, 2026
Read more

Cloud and core infrastructure frameworks in Security Profile

Mark Barber July 29, 2026
Read more

Complete questionnaires without closing remediation

Mark Barber July 15, 2026
Read more

Company name aliases for smarter detection

Mark Barber July 1, 2026
Read more

FortiBleed Exposure Detection

Mark Barber June 25, 2026
Read more

Updated application usage policy controls

Mark Barber June 17, 2026
Read more
View all release notes

See UpGuard In Action

Book a free, personalized onboarding call with one of our cybersecurity experts.
Free instant security score

How secure is your organization?

Request a free cybersecurity report to discover key risks on your website, email, network, and brand.
Website Security scan results table Cyber security rating score 850 out of 950