Release notes

Workflow enhancement – streamlined threat triage

Mark Barber November 6, 2025
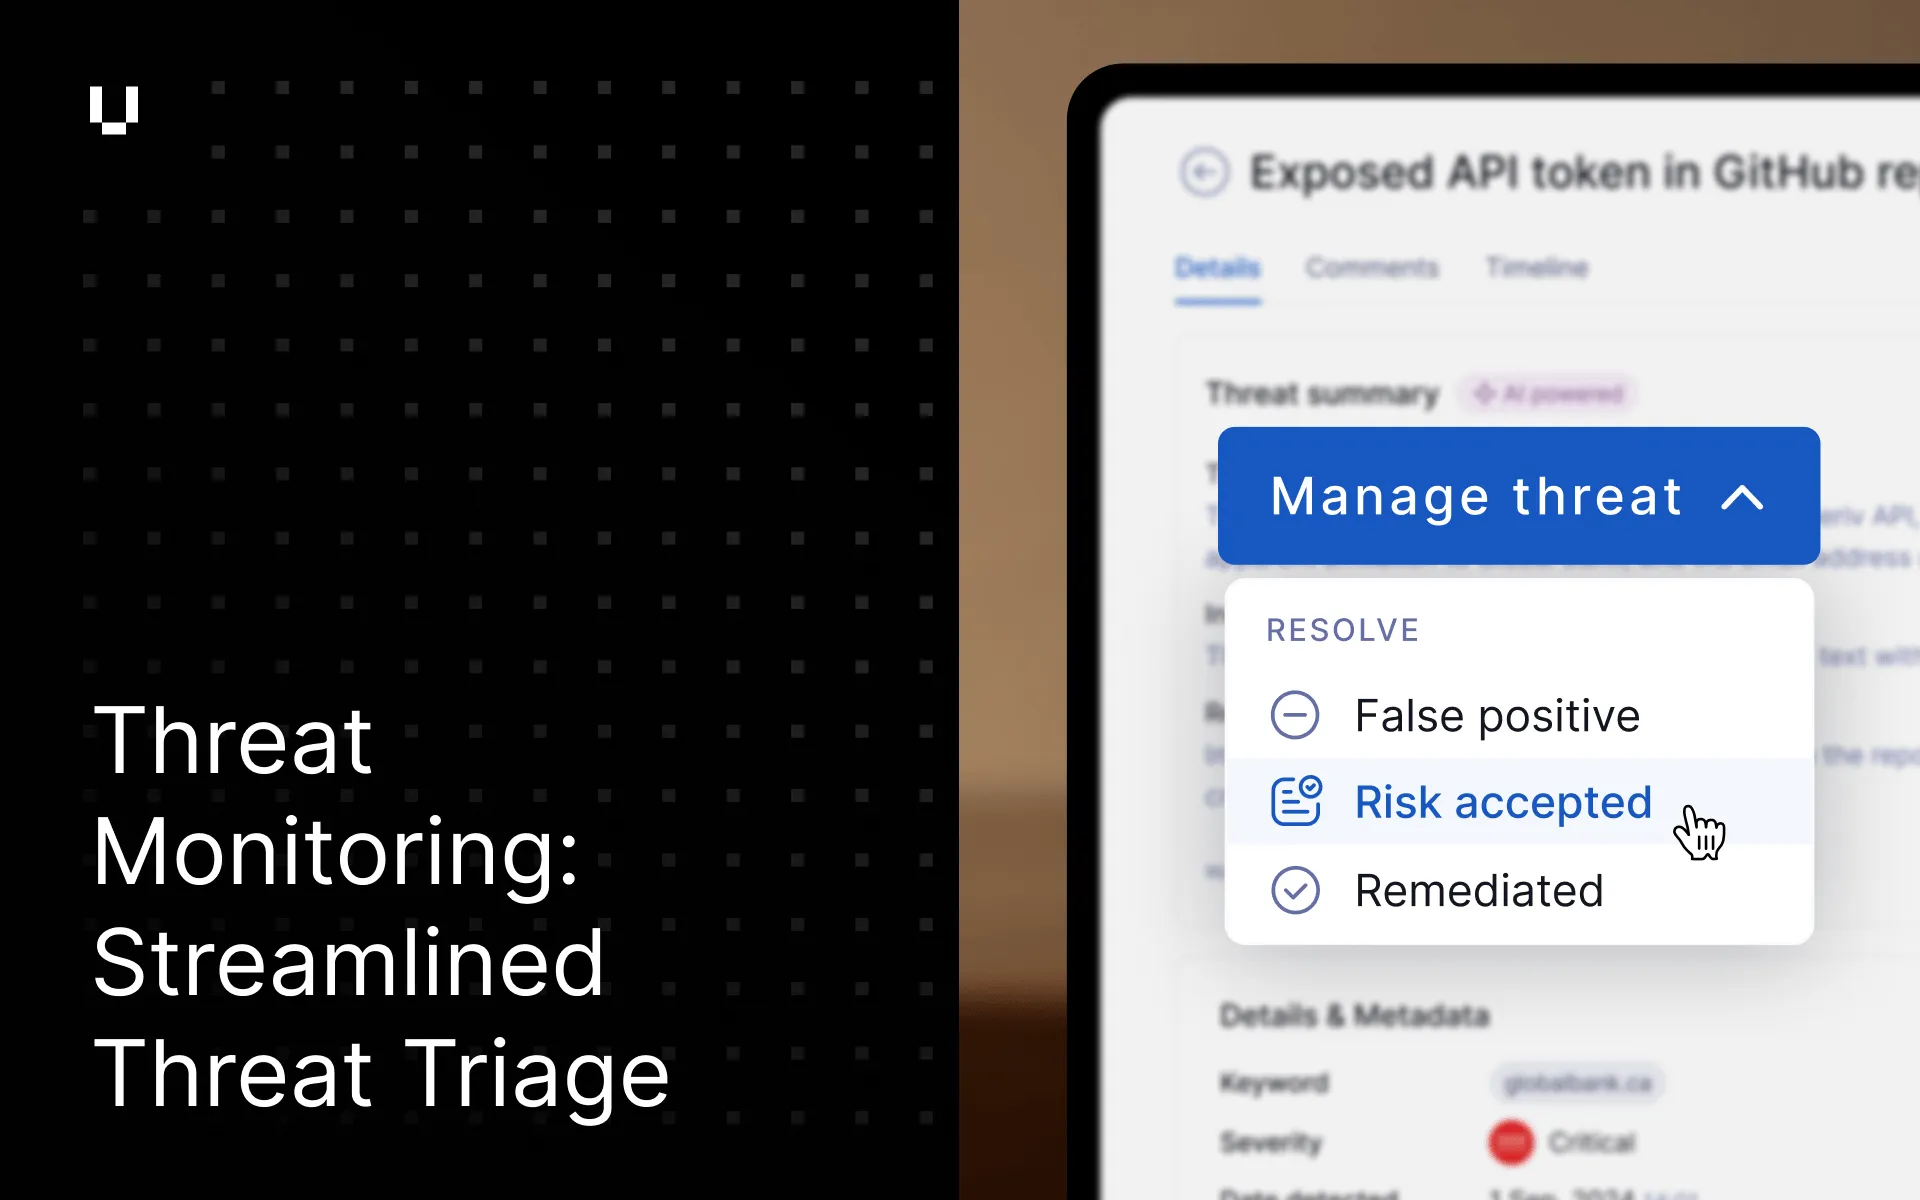
We’ve enhanced the Threat Management workflow to make it simpler, faster, and more precise. The new layout enhances usability while capturing richer context on how analysts classify and resolve threats.

Key improvements include:

  • A single “Manage Threat” dropdown now consolidates all key actions for easier access.
  • Actions are grouped under two clear sections: “Collaborate” and “Resolve”, aligning with how analysts naturally work through findings.
  • The term “Dismiss” has been renamed to “False Positive” to clarify intent and improve tracking of analyst decisions.
  • A new “Risk Accepted” action allows users to distinguish between legitimate but accepted risks and false alerts.
  • “Close as Remediated” is now “Remediated”, improving consistency across the workflow.
  • The ability to page through threats now sits in the top navigation bar, making navigation more intuitive. When a threat is resolved, the system automatically advances to the next open threat.
  • The header is now sticky, with a full-width divider for easier readability as you scroll.
  • We’ve also relocated comments to their own tab to provide users with more space to review and collaborate on the details.

These changes make the workflow more intuitive to use while ensuring every analyst action contributes to greater fidelity and insight in our threat intelligence feedback loop.

New Risk: Infostealer malware detected for Vendor Risk

A new risk, “Infostealer Malware Detected,” will now be raised for tiered vendors when data indicates a potential breach from infostealer malware. This high-severity risk helps identify data leakage threats from your vendors. To help users proactively address these items before they impact scores these new risks will initially be flagged as “provisional” until January 2026.

Expanded vendor security document coverage

Our monthly import of public vendor security documents has expanded coverage to include 298 new documents, enhancing the data available in Vendor Security Profiles.

Trial Breach Risk to automate your Security posture in Trust Exchange

Users can now trial Breach Risk in order to enable continuous monitoring for their Trust Exchange security profile, enabling users to improve their security profile and posture with automated score improvements. Breach Risk can then be purchased after the 14 day trial period.

Other improvements

  • To better classify upcoming risks, the “Brand Reputation” risk category has been renamed to “Operational Risk”.
  • To localise Trust Page settings, the Custom Domain configuration has been moved from General Settings (cogwheel) to “Trust Page -> Settings and More”.
  • This release includes a number of bug fixes.
View all release notes

UpGuard Release Notes

Learn about new features, changes, and improvements to UpGuard.

Brand impersonation detection across mobile app stores

Mark Barber September 9, 2026
Read more

Clearer citations and timeline for Security Profile checks

Mark Barber August 26, 2026
Read more

Subprocessors in Trust Center

Mark Barber August 12, 2026
Read more

Cloud and core infrastructure frameworks in Security Profile

Mark Barber July 29, 2026
Read more

Complete questionnaires without closing remediation

Mark Barber July 15, 2026
Read more

Company name aliases for smarter detection

Mark Barber July 1, 2026
Read more

FortiBleed Exposure Detection

Mark Barber June 25, 2026
Read more

Updated application usage policy controls

Mark Barber June 17, 2026
Read more
View all release notes

See UpGuard In Action

Book a free, personalized onboarding call with one of our cybersecurity experts.
Free instant security score

How secure is your organization?

Request a free cybersecurity report to discover key risks on your website, email, network, and brand.
Website Security scan results table Cyber security rating score 850 out of 950