Release notes
Remediate risks faster with built-in guidance

Toby Roger September 25, 2024
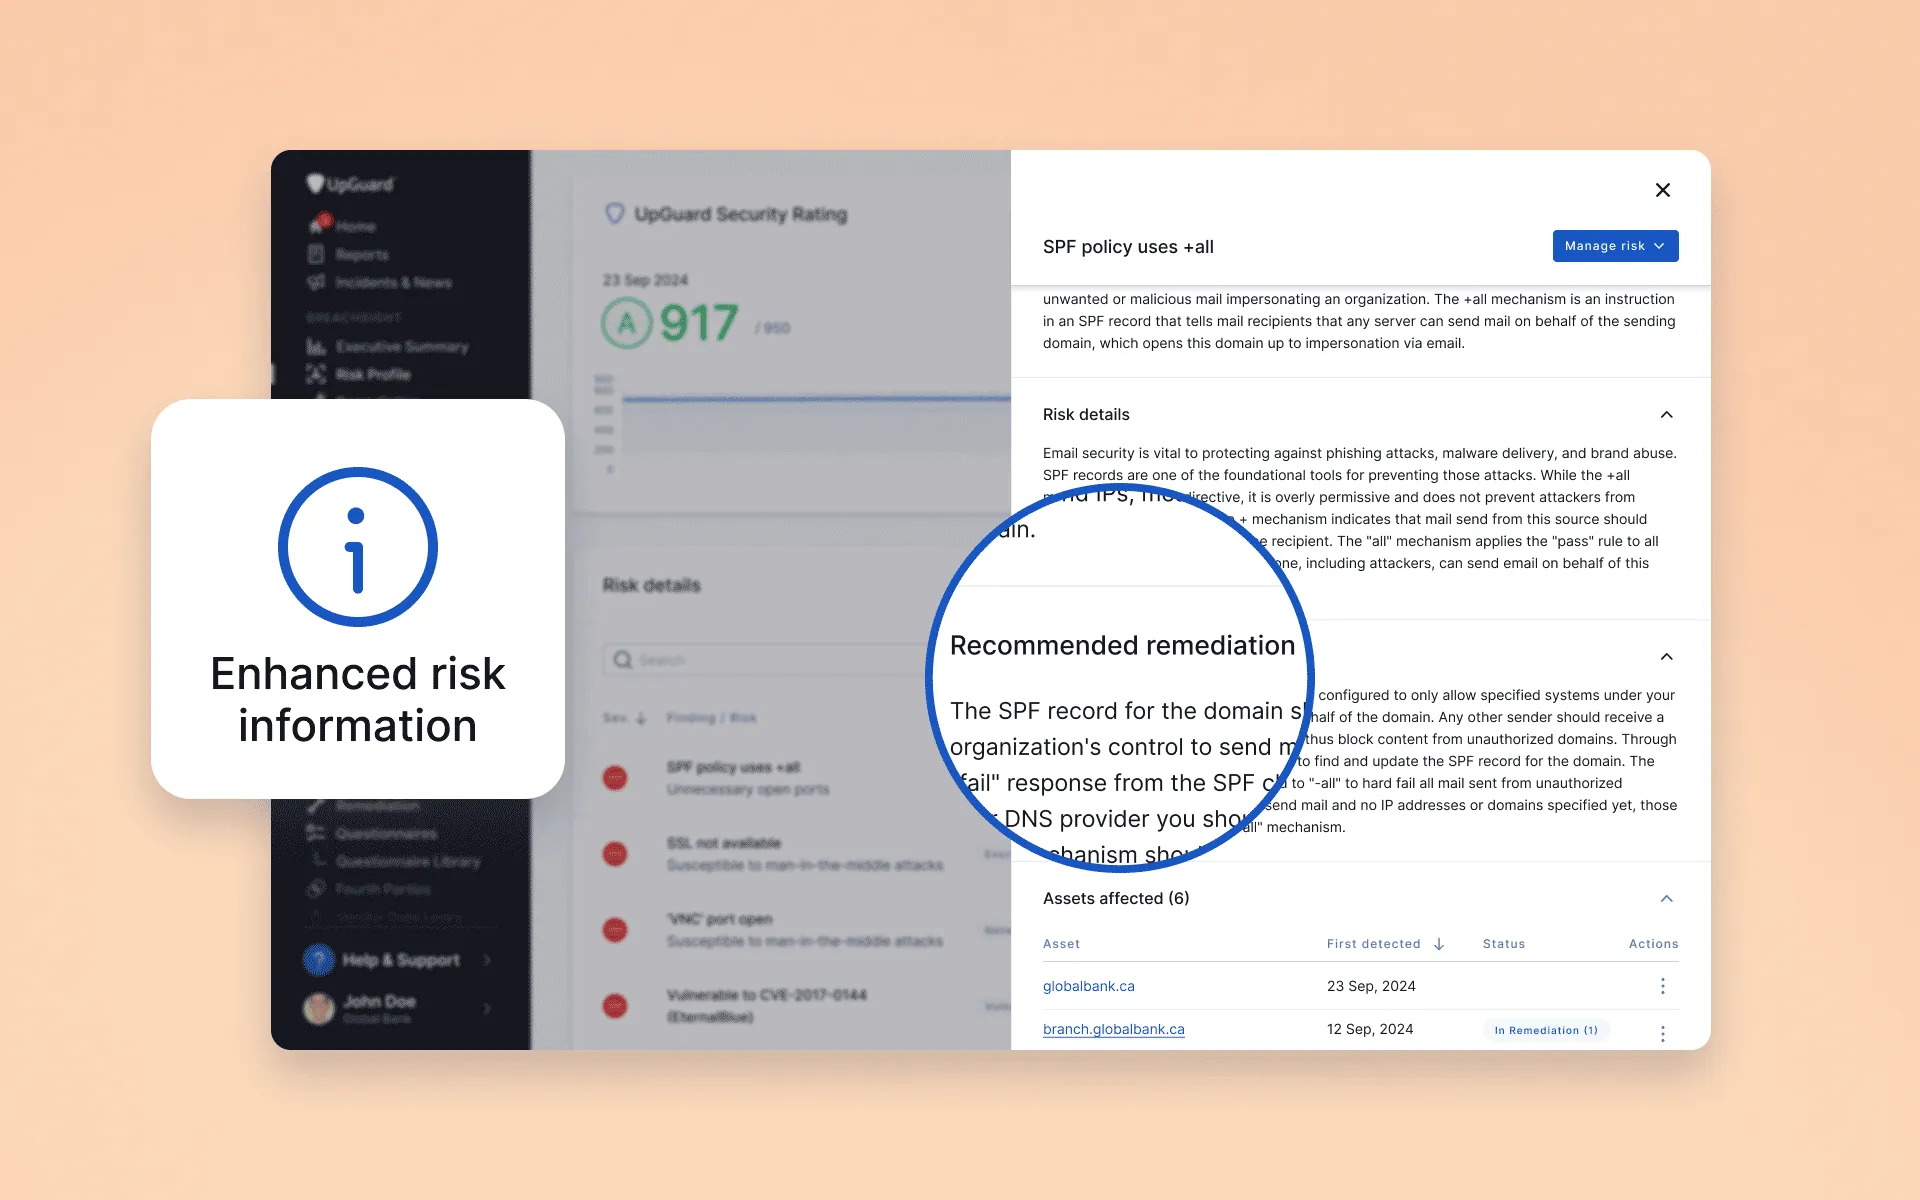
We’re making it easier to understand and explain web risks by introducing Risk Remediation Guidance to Breach Risk and Vendor Risk. This update offers detailed explanations of each risk, its importance, and how to remediate it, enabling swift action even for non-technical users. With Risk Remediation Guidance, Breach Risk users can act more decisively, resolving risks efficiently with clear instructions, while vendors gain deeper insights to better understand and mitigate risks.
We’ve introduced a new questionnaire to assess an organization’s adherence to the Digital Operational Resilience Act in the EU. In effect from January 17 2025, DORA addresses gaps in EU financial regulation by requiring financial institutions to manage ICT-related risks and operational resilience alongside traditional capital allocation for risk management.
Vendor Snapshots (previously Instant Reports) allow you to view the external risks of an organization for 30 days without adding it to your monitored vendor list. It’s perfect for when you need a point-in-time view of a vendor’s security posture, such as when assessing or comparing potential vendors as part of a due diligence process.
Improvements that have been implemented as part of this release:
To learn more see What is the difference between a Vendor Snapshot and a Monitored vendor?
Our web scanner now detects client-side and server-side configuration leaks, enhancing protection against exposed API keys and configuration files. This update strengthens Breach Risk and Vendor Risk by improving proactive risk detection for customers and their vendors.