Reducing Supply Chain Security Risks with Vendor Segmentation

Security teams often spend the same assessment effort on a commodity SaaS tool as they do on a critical enterprise resource planning integration. That mismatch leaves high-exposure suppliers under-watched while low-stakes vendors consume the queue.
Vendor segmentation isolates which third parties can do the most damage to your organization if attackers compromise them, so assessment depth and monitoring intensity match exposure. In a cyber supply chain risk management (C-SCRM) program, you group suppliers on a business impact and security risk matrix and put remediation effort where interruption or data loss would produce the worst consequences.
Without that supplier split, teams either over-assess every supplier or miss the few vendors that can halt operations or leak sensitive data.
Peter Kraljic's 1983 Harvard Business Review article mapped profit impact against supply risk for purchasing strategy. You can use a security remap of this matrix that keeps the four-box structure and changes what each axis measures to segment your vendor list.
What is the Kraljic security-risk matrix, and how can it apply to vendor segmentation?
The most common error we see in the Kraljic security-risk matrix is scoring the original procurement axes and inverting which quadrant is critical. That inversion mis-tiers questionnaires, continuous monitoring, and the executive reporting that follows. The fix is a vendor segmentation matrix with two explicit axes and four distinct actions.
Business impact (the y-axis) answers how badly operations or revenue suffer if the vendor fails or is breached, especially where regulated data is in play. Security risk (the x-axis) answers how severe a cyber compromise looks given posture, access sensitivity, and replaceability.
Mapped together, those two axes produce four quadrants, each with its own action:
Critical, irreplaceable vendors sit in quadrant two, not quadrant one. Quadrant one is high security risk with low business impact. Those relationships are candidates for accelerated remediate-or-replace decisions.
Quadrant two couples high impact with high exposure, so you can't casually offboard the supplier. You intensify assurance instead. Quadrant three keeps continuity focus when impact is high, but current security risk is low. Quadrant four stays lightweight so analysts don't spend time on low-stakes commodity tools.
Place every in-scope third party on the grid before you add any process on top of it. If two teams disagree on a vendor's cell, the dispute is usually about incomplete impact language or missing security evidence, not about the matrix itself. Document the scoring inputs so auditors can trace why a supplier landed in quadrant two rather than quadrant three.
Score security risk from evidence your team already collects in third-party risk work, including questionnaire and control findings, external posture, access to sensitive systems or data, and concentration of dependency on the vendor's own suppliers. The matrix turns that evidence into a ranked work queue inside C-SCRM rather than a flat vendor list.
How do you identify high-risk vendors in a supply chain?
Map each vendor on the business impact and security-risk matrix. Quadrant one (high security risk, replaceable) and quadrant two (high impact and high security risk, irreplaceable) form the high-risk set. Quadrant two needs the deepest assessment, most frequent review cadence, and most intensive monitoring because your organization depends on the vendor and the exposure is material.
Treat security risk as high when the vendor holds sensitive data or system access, your team can't replace them quickly, external posture looks weak, or fourth-party dependency would widen blast radius. Treat business impact as high for revenue-critical workflows or regulated data paths, especially when the vendor is also a single point of failure in production operations.
Quadrant three and quadrant four still matter for program completeness, but they aren't the high-risk set. Quadrant three needs continuity planning and scheduled review so a low-exposure strategic supplier doesn't accumulate new access. Quadrant four should stay lightweight so commodity tools don’t carry the same evidence burden as a payment processor or core cloud platform.
Once those labels exist, the operational split is clear. For quadrant one, accelerate remediate-or-replace decisions so a noisy, low-value relationship doesn't keep consuming monitoring budget.
For quadrant two, lock in more in-depth questionnaires and tighter residual-risk review, and back both with continuous monitoring that updates vendor risk as posture changes.
Four methods for applying vendor segmentation
The matrix decides who is high risk. Day-to-day control comes from four methods that enforce different intensity without trapping the program in spreadsheets: tiering, portfolios, labels, and custom vendor attributes.
You'll get the most out of this vendor segmentation model with a vendor risk management (VRM) platform that can support it. We’re referencing the segmentation features in UpGuard Vendor Risk to illustrate how to apply this model to your third-party risk mitigation workflow.
Tiering
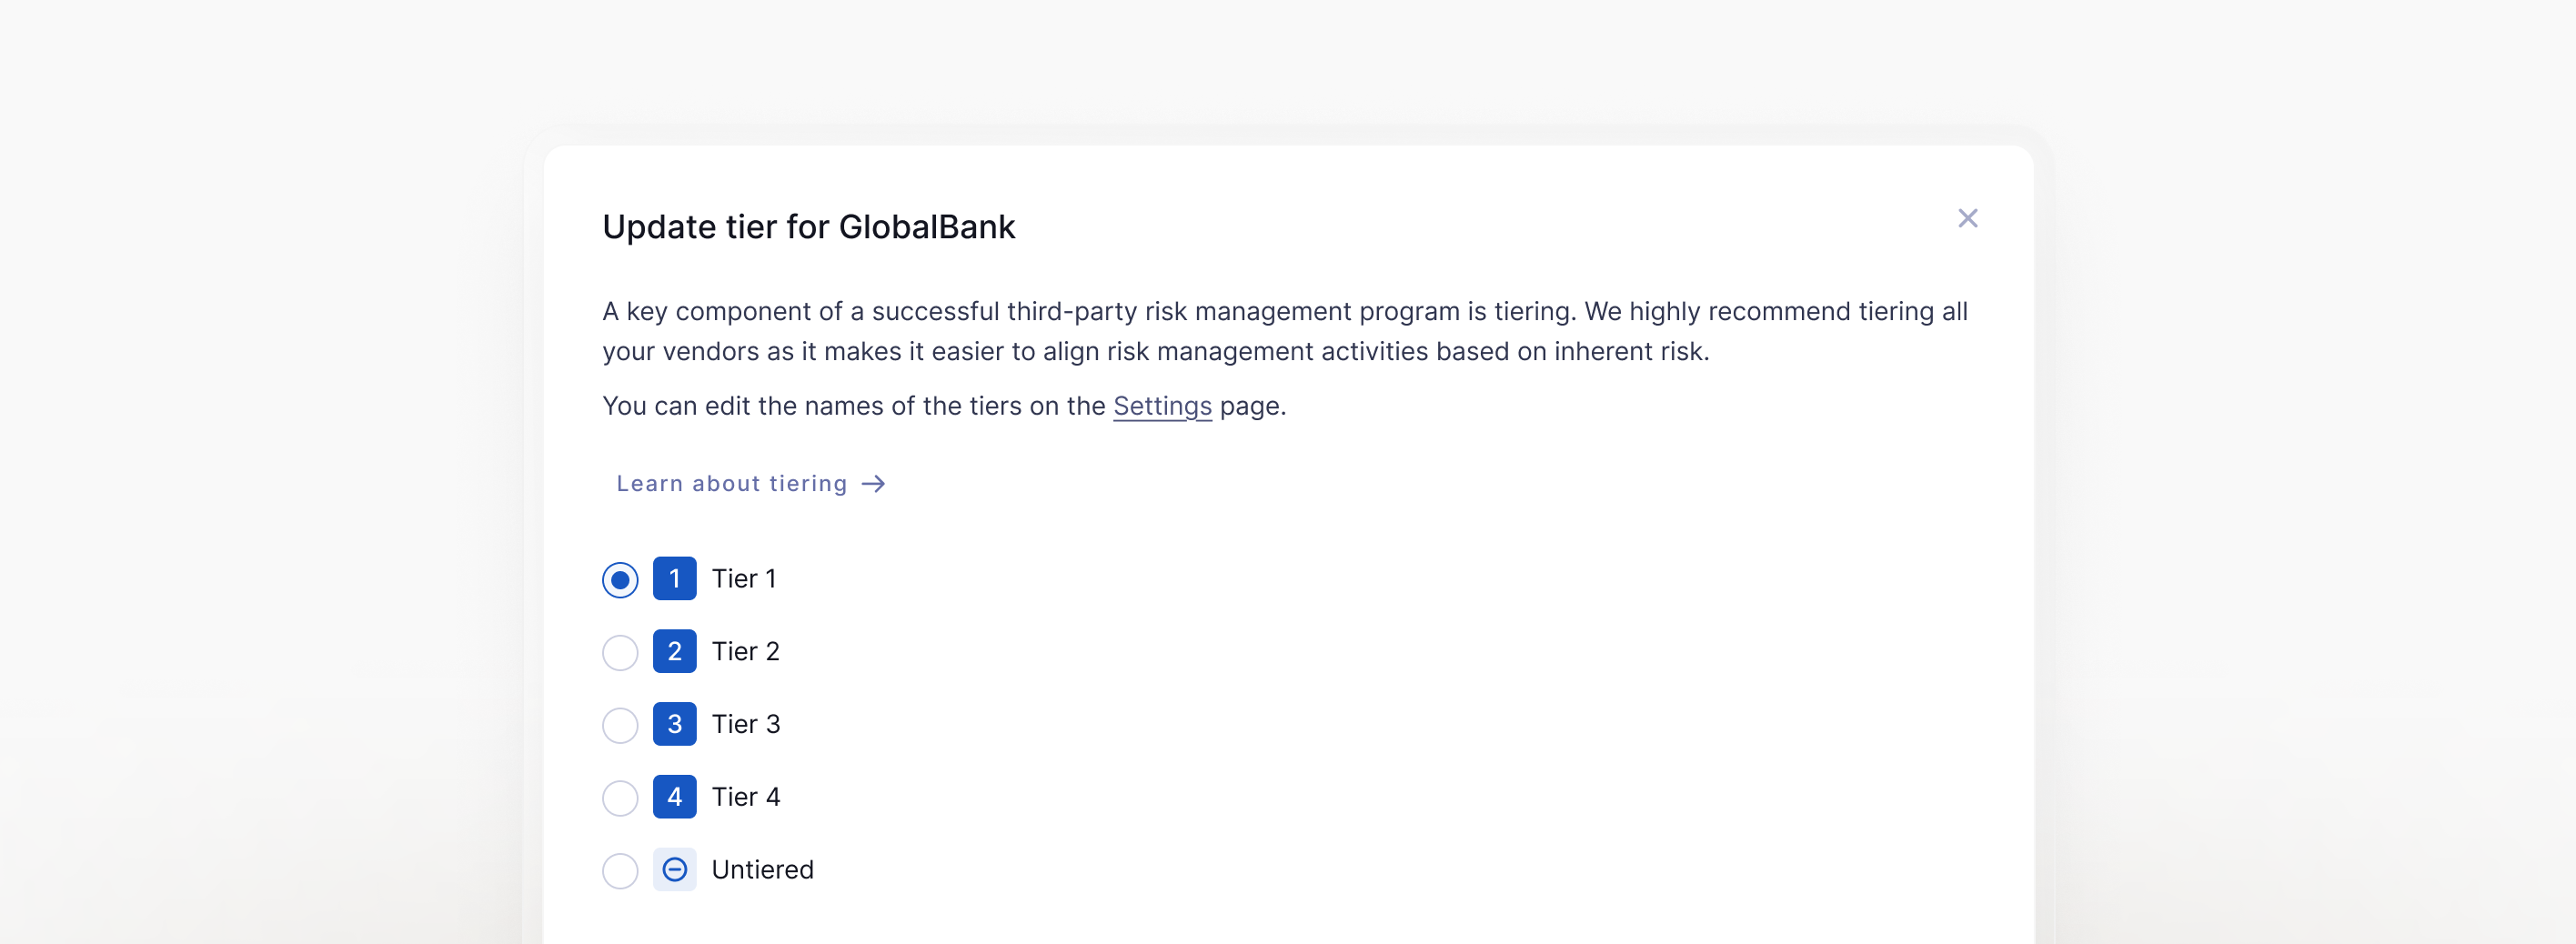
Vendor tiering assigns assessment depth and review frequency by criticality band. For example, lower tiers receive lighter, less frequent checks.
Tiering is the operational expression of the matrix. Once you set a vendor's band, cadence and evidence requirements follow it, not ad hoc judgment on every ticket. Common criteria include data sensitivity, system access, replaceability, and residual risk after controls.
The trade-off is governance cost, as too many tiers recreate one-off treatment. Too few force high-impact suppliers into the same queue as commodity tools. Most mid-market C-SCRM programs start with three or four tiers tied directly to matrix cells, then adjust after one review cycle.
Portfolios
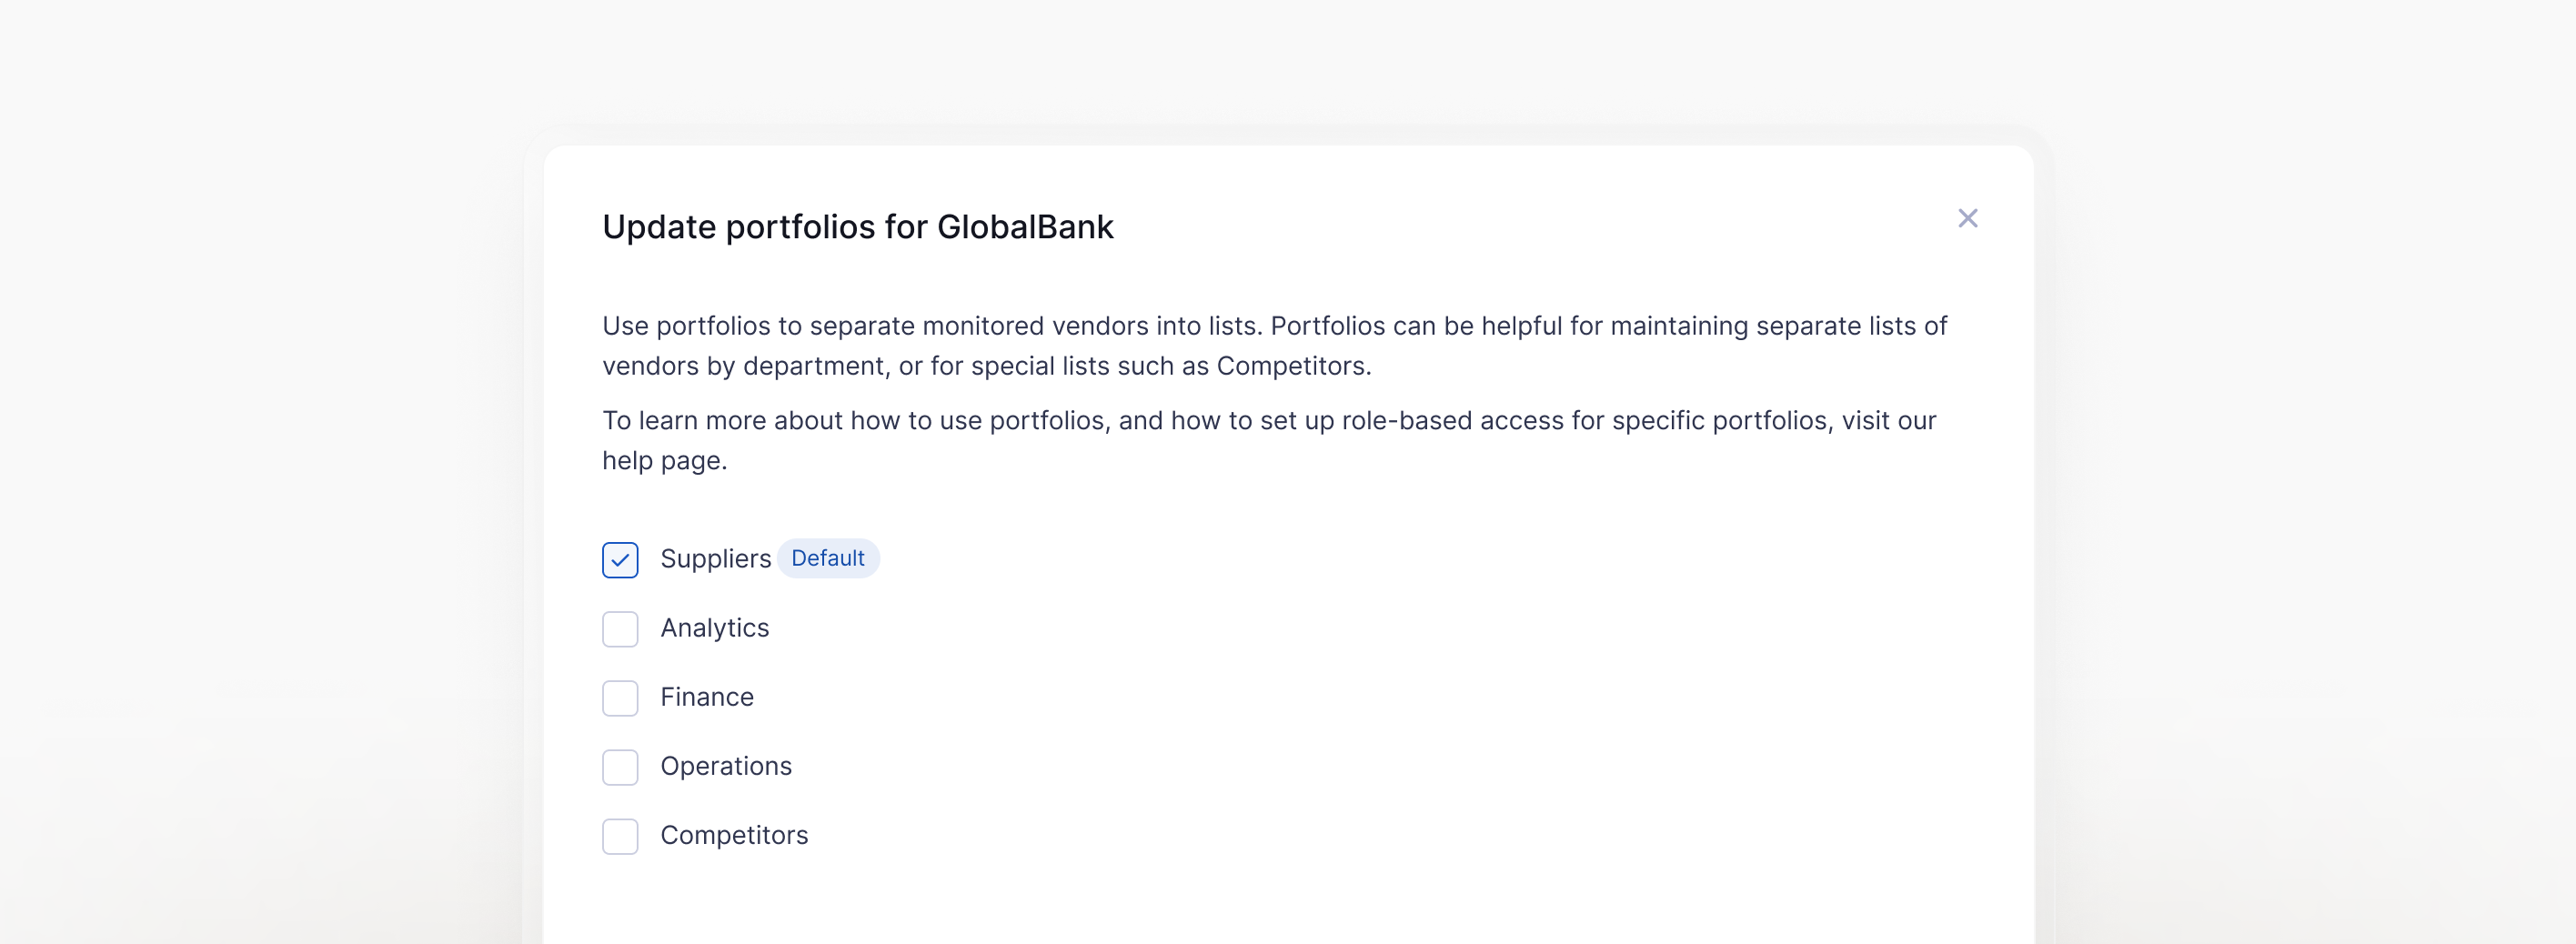
Portfolios segment the vendor ecosystem by owner or business unit so risk registers and remediation owners stay clear. When finance, IT, and other departments each sponsor different supplier sets, portfolio views keep findings from landing on a generic shared queue nobody owns.
Structure portfolios around how the business already assigns budget and system ownership. A portfolio owner should be able to accept residual risk, drive remediation, and speak to leadership about that portion of the supply chain.
Segmentation without clear ownership fails audits even when the matrix labels are right. Portfolios also support department-level risk registers when you implement C-SCRM along with an existing security framework.
Labels
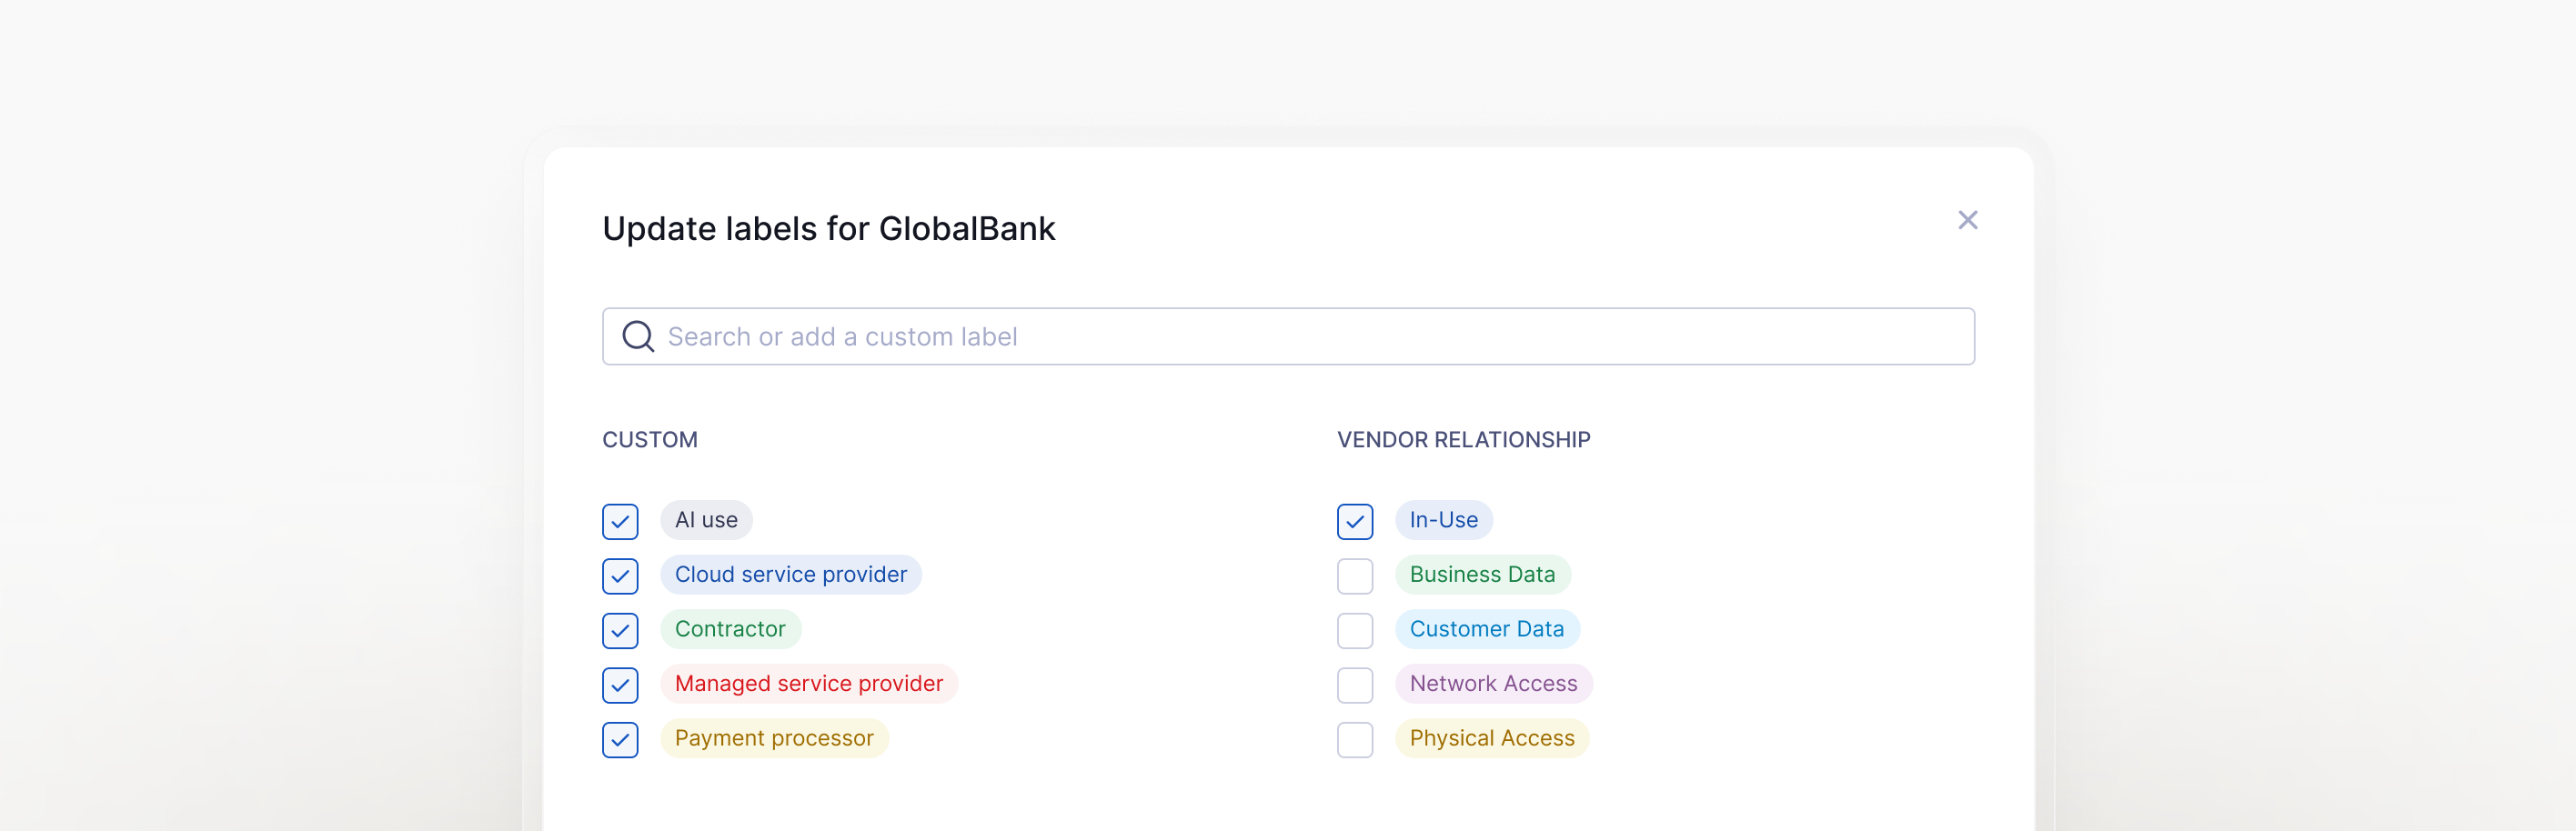
Labels tag lifecycle state or matrix quadrant (onboarding, in use, quadrant one, quadrant two, offboarding) so analysts can filter fast during incidents and board preparation. A breach notification that requires "all quadrant two vendors with production data access" should be a saved view.
Govern labels with a short controlled vocabulary. Prefer matrix cells and lifecycle states over free-text tags that drift. Labels differ from tier: tiers set intensity, labels make those intensity decisions searchable under time pressure.
Review labels when vendors move between onboarding, in use, and offboarding so filters stay trustworthy during incident response.
Custom vendor attributes
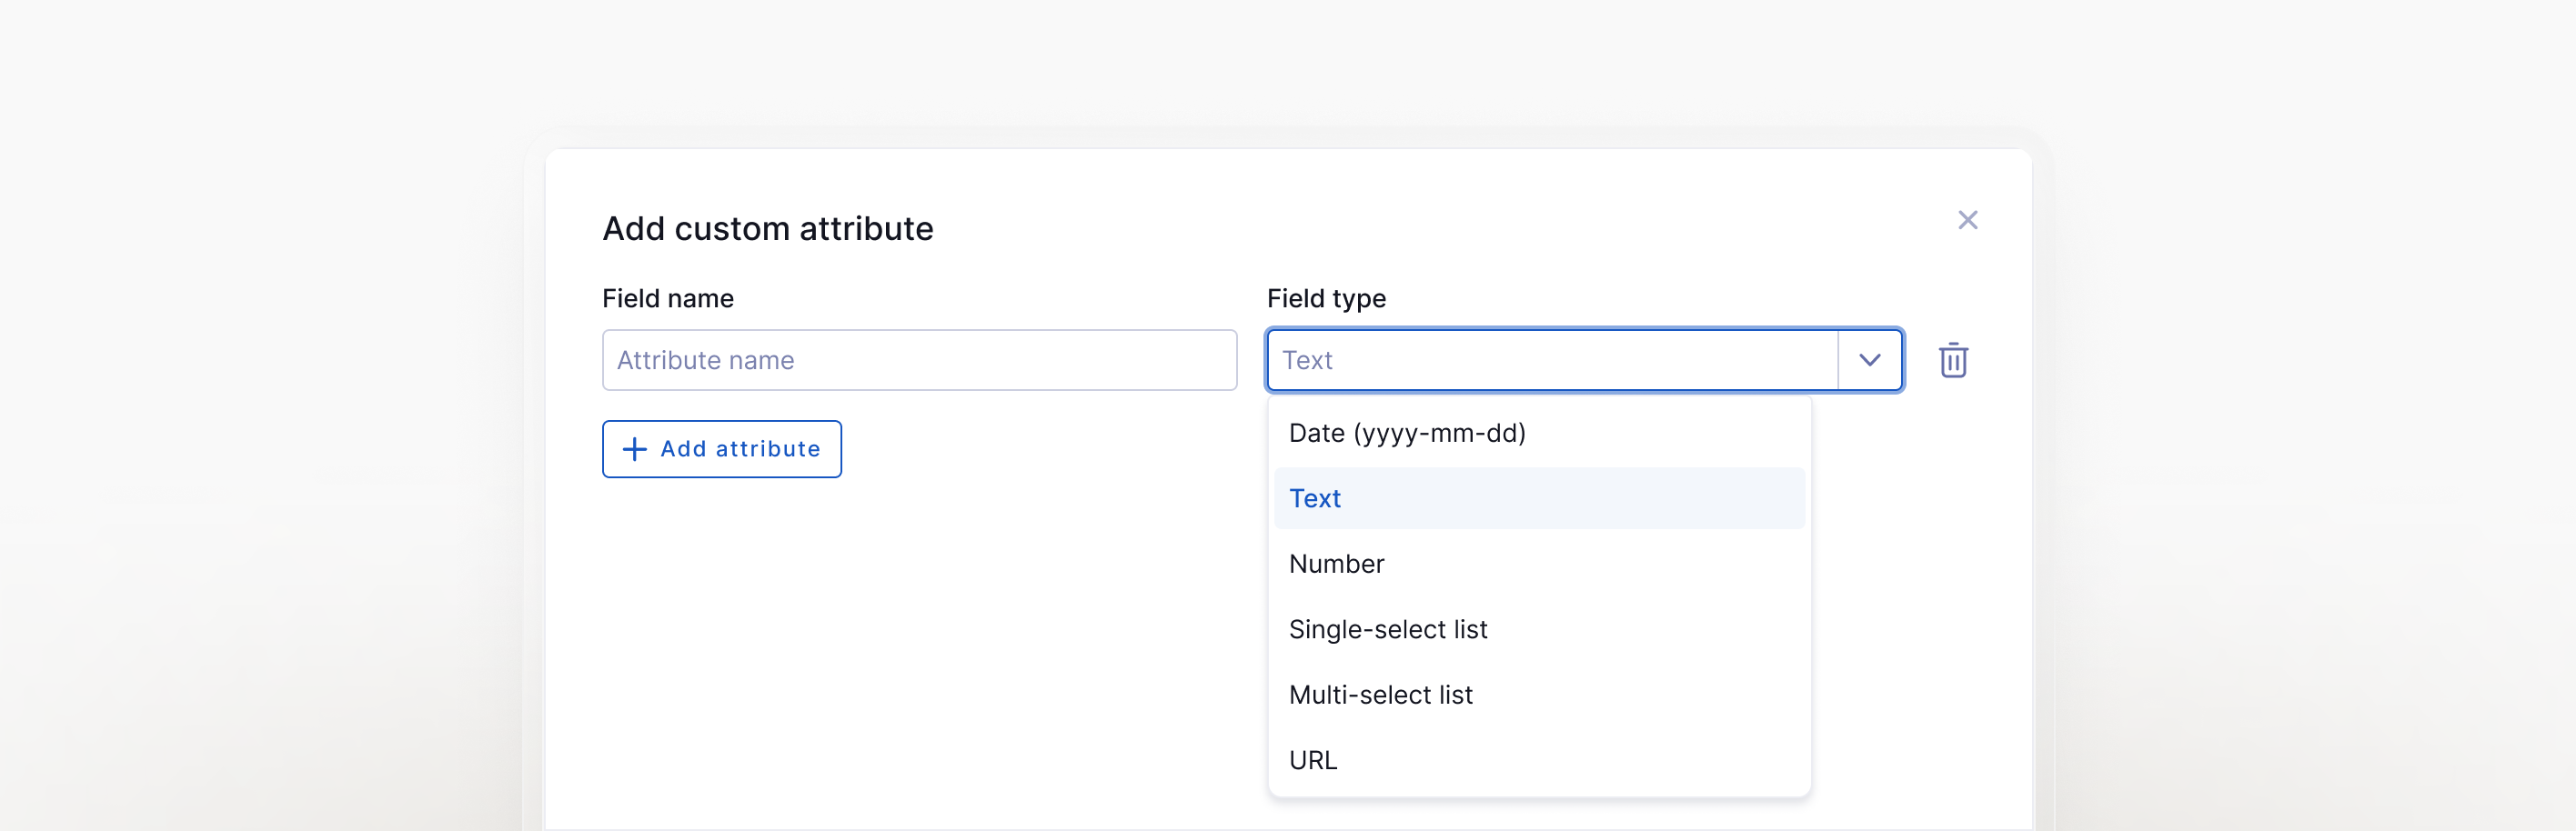
Custom vendor attributes store structured fields that flat tags can't carry cleanly, such as data access class, authentication level, business owner, expected offboard date, and AI-in-supply-chain flags.
Reporting and search then answer precise questions, such as which quadrant two vendors process regulated data under single sign-on exceptions, without creating a new spreadsheet for every audit.
Design attributes with validation rules and a clear owner for each field. If nobody maintains the value, the attribute becomes noise. Use attributes in onboarding checklists, residual-risk approvals, and offboarding access removal.
Attributes turn segmentation into queryable program data. Use them with tiers and labels, not as a substitute for either.
What to do once you’ve segmented your vendors
C-SCRM programs also need to account for fourth-party dependency when high-risk labels depend on a vendor's own suppliers. Standards such as NIST SP 800-161 guide organizations to identify, assess, and mitigate cybersecurity supply chain risk across the lifecycle.
Segmentation turns that guidance into a ranked work queue within C-SCRM. After you implement the four methods, map tiers to inherent risk with an objective scoring model and tighten operating habits so cadence doesn't drift.
Re-segment when access or criticality changes, or when posture shifts materially. Segmentation is a living configuration, not a one-time workshop.
What tools help with vendor segmentation and tiering?
The tool class that supports vendor segmentation and tiering is a VRM platform that discovers and onboards vendors, then assigns tiers, portfolios, labels, and custom attributes.
For specific VRM tool shortlists and service comparisons, see the vendor risk management software list.
At scale, the methods only work if monitoring and assessment capacity match the tier map. Platforms that can segment and continuously monitor risk signals make the matrix enforceable across large vendor rosters.
Segmenting vendors with UpGuard
UpGuard Vendor Risk supports all four methods:
- Custom vendor attributes: Filter by contract details, account owners, and critical supply chain security data to locate information faster.
- Vendor tiering: Find the vendors that could damage your security posture most, and review them first.
- Vendor portfolios: Group vendors by the departments they serve to simplify access control management and risk register monitoring.
- Vendor labels: Locate vendors by key security characteristics to speed up critical risk remediation.
A global airline used UpGuard to keep more than 4,300 vendors under continuous monitoring and cut vendor assessment time by up to 75%. That’s what segmented intensity looks like when the roster is too large for uniform manual review.
For a tailored walkthrough of how you can use UpGuard Vendor Risk to segment your own vendor list, book a demo. Our team will answer any questions you have about how the platform uses tiering, portfolios, labels, and custom vendor attributes to reduce supply chain security risks.
Related posts
The Evidence Is In: UpGuard Named a Leader in the IDC MarketScape for Worldwide Third-Party Risk Management
